PHISHING INDEX
Below are the most common email phishing attempts detected by the TG Soft Anti-Malware Research Center in
June 2026:
22/06/2026 =>
Microsoft
19/06/2026 =>
TISCALI
17/06/2026 =>
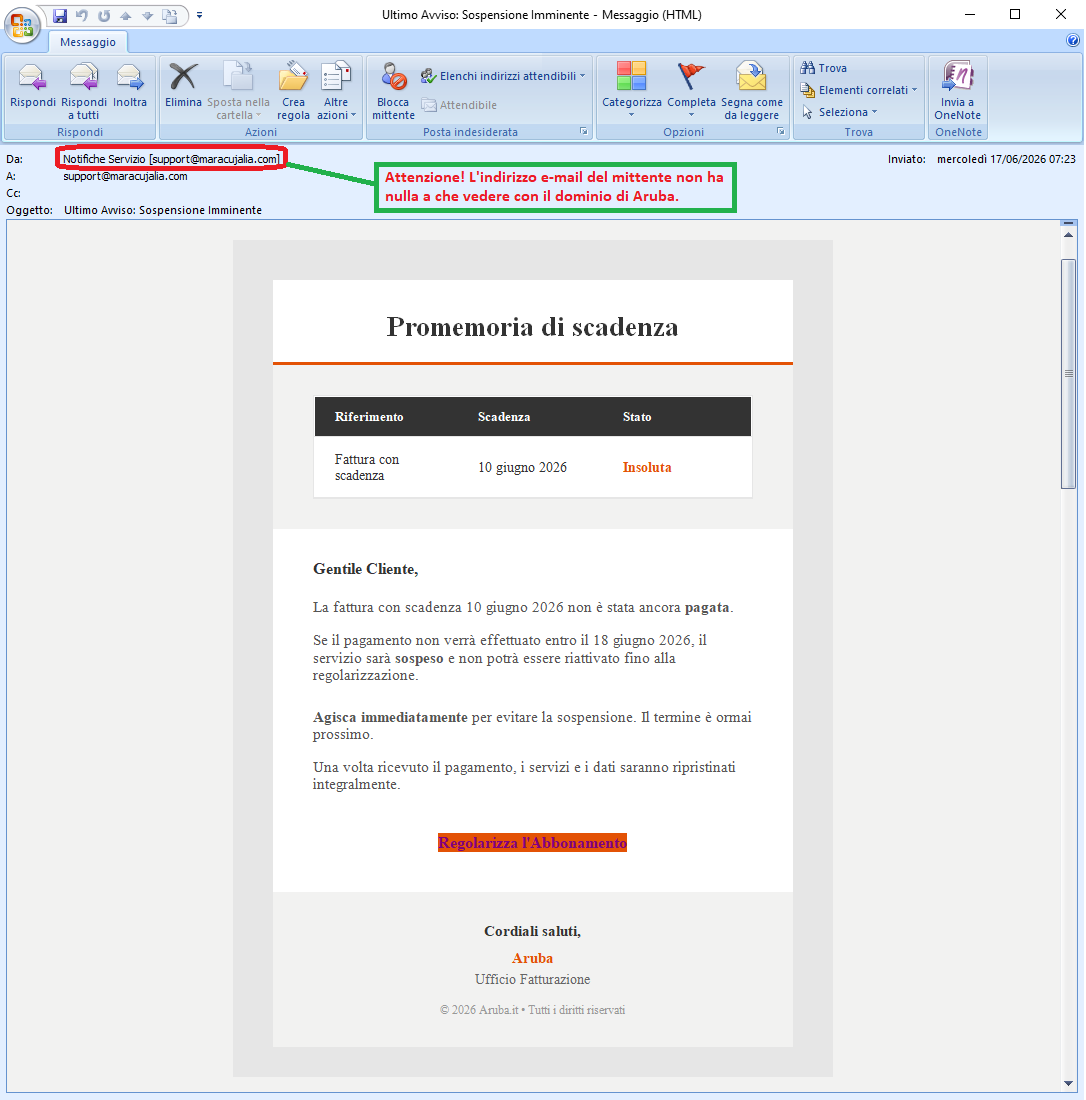
Aruba - Final notice
14/06/2026 =>
Bank
12/06/2026 =>
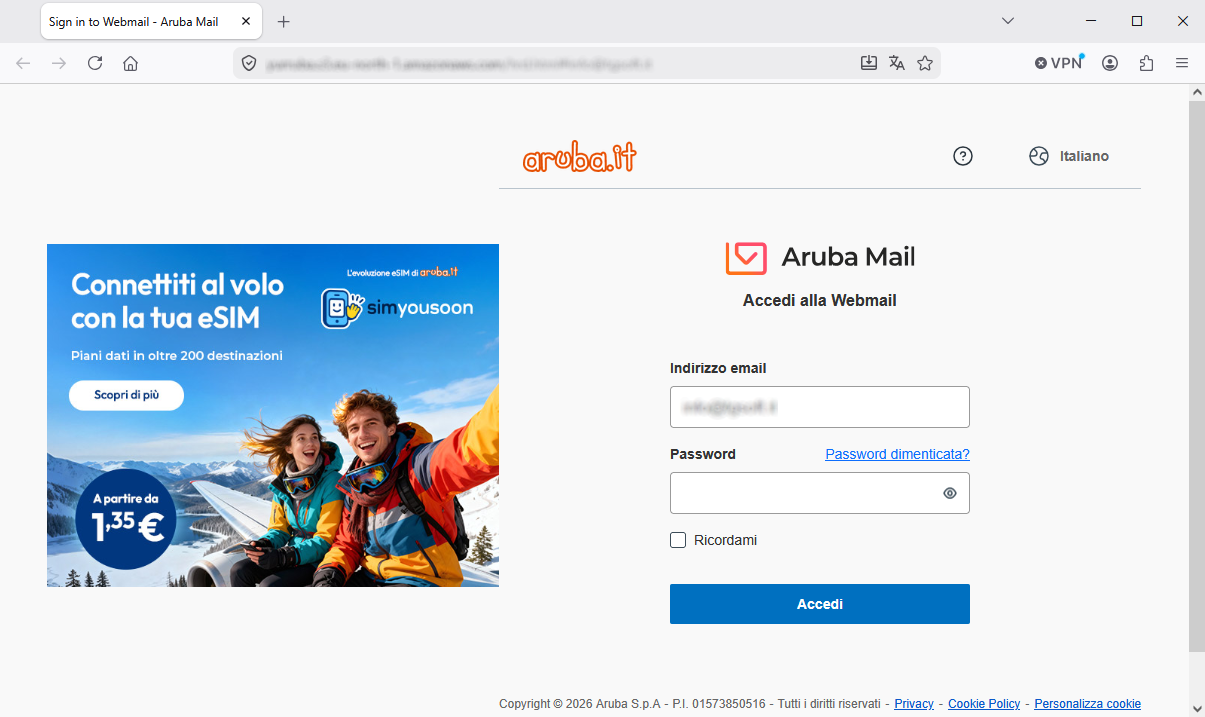
Aruba - Log in from a new device
12/06/2026 =>
Email account
08/06/2026 =>
PagoPA
02/06/2026 =>
BPM
02/06/2026 =>
Aruba
01/06/2026 =>
Aruba - Unpaid invoice
01/06/2026 =>
DHL
These emails aim to deceive unsuspecting victims into providing sensitive information, such as bank account details, credit card codes, or personal login credentials, with all the easily imaginable consequences.
22 June 2026 ==> Phishing Microsoft
SUBJECT: <
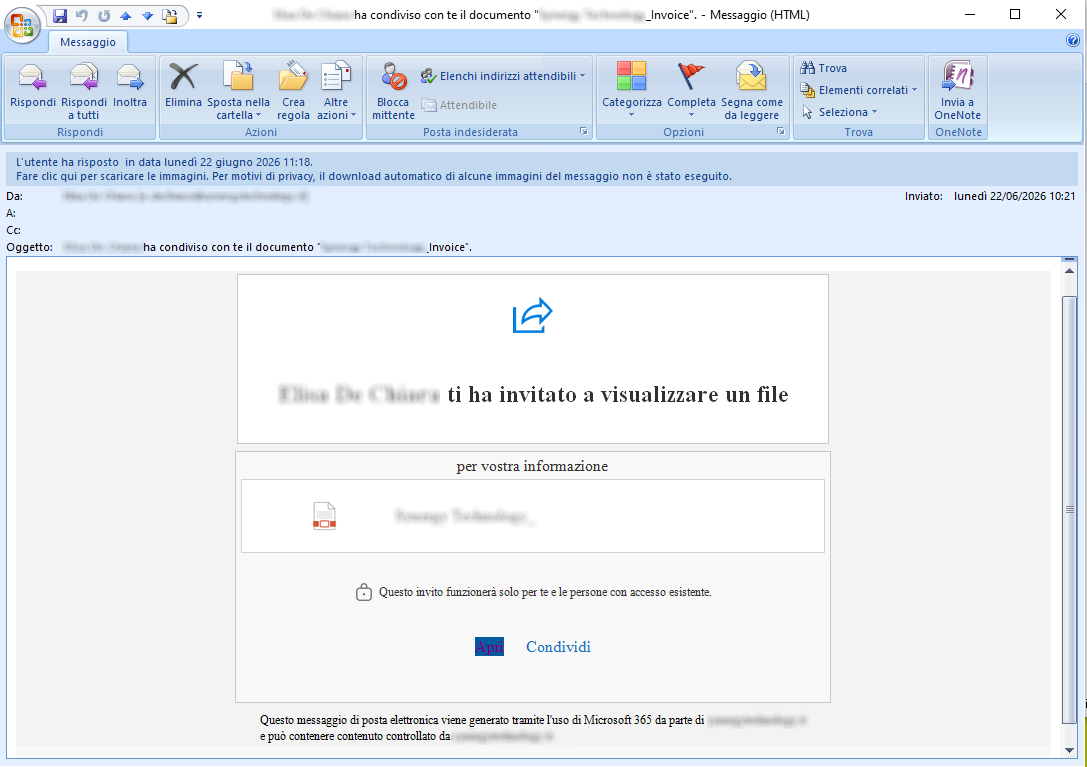
***** has shared the document ‘****_Invoice’ with you".>
Below, we analyse the phishing attempt aimed at stealing
Microsoft account credentials.
The message informs the recipient that they have received a file named ‘***_Invoice’, which refers to an invoice sent by one of their suppliers or customers. It then invites them to download and open the file via the following link:
Apri
If we examine the email, we can see that the cybercriminal was careful enough to use – probably via a label – the email address of the supplier or customer who sent the attached file. All this is done to make the message seem more credible, thereby leading the recipient – who sees the email coming directly from one of their own suppliers or customers – to trust it and click on the link.
Anyone who unfortunately clicks on the
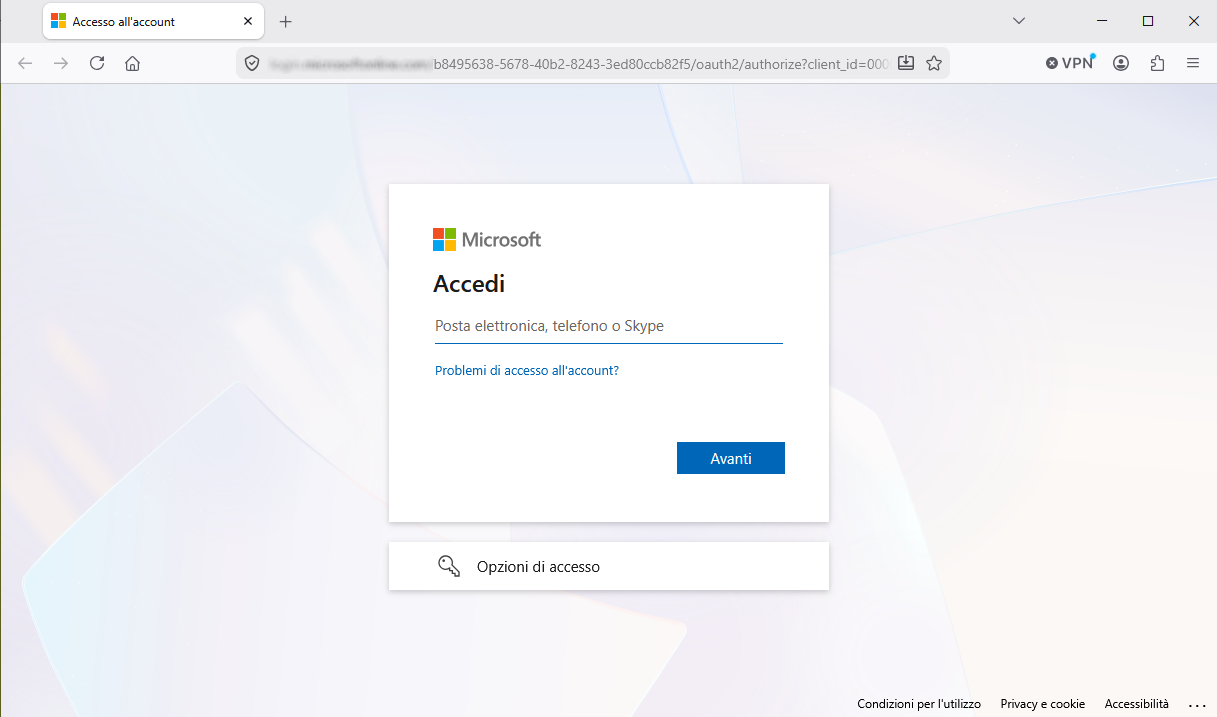
Open link will be redirected to a suspicious web page – which is visually well-designed – where they are asked to log in to their
Microsoft account in order to download the file mentioned in the message.
However, the page where you are redirected is hosted on an unusual address/domain:
https[:]//[FakeDomainName*].com/.....
We urge you to always be careful and never enter your personal details and/or passwords into forms hosted on fake websites, as these will be sent to a remote server and used by cybercriminals, with all the associated risks easy to imagine.
19 June 2026 ==> Phishing Tiscali
SUBJECT: <
🚫(TISCALI! Email Deactivation)>
Below, we analyse a phishing attempt aimed at stealing login credentials for
TISCALI accounts.
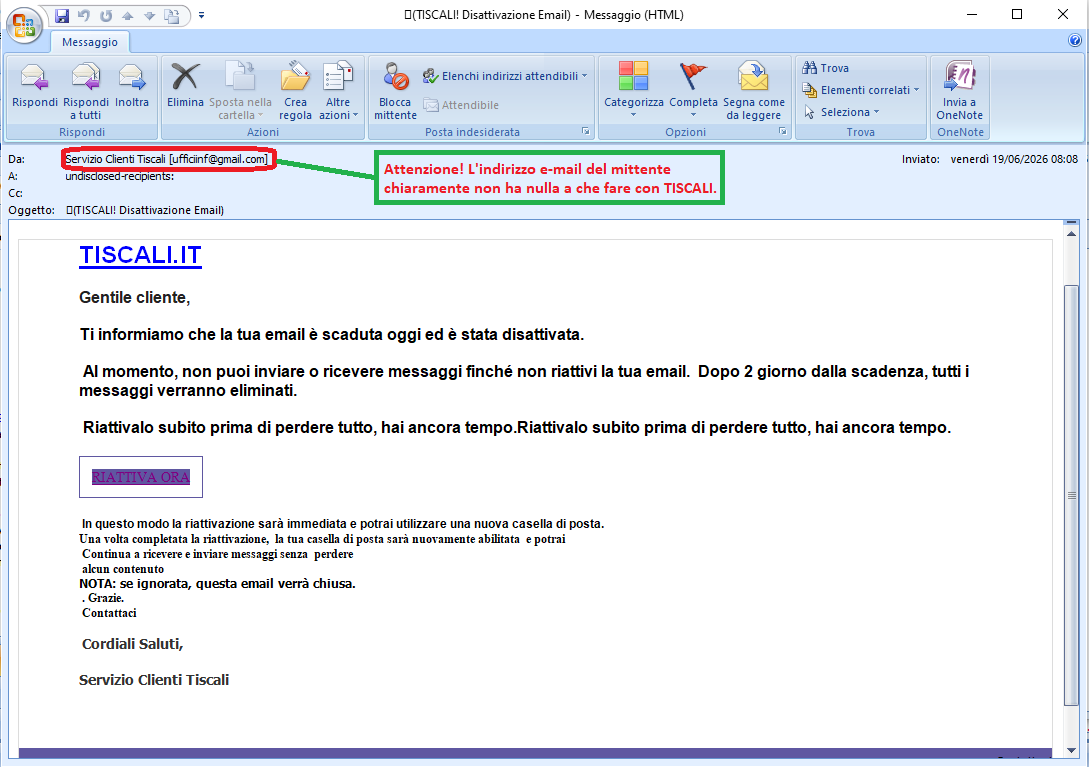
The message informs the recipient that their email account has expired and has been deactivated; it is therefore no longer possible to send or receive messages, at least until it is reactivated. The email also warns the user that, one day after the expiry date, all messages will be deleted.
The user is therefore asked to reactivate their account via the following link as soon as possible, and in any case within 2 days, to avoid losing all their messages.
REACTIVATE NOW
On closer inspection of the message, there are a number of clues that should raise suspicions. We immediately notice that the email address of the message <
ufficiinf[at]gmail[dot]com> cannot be traced back to the official
TISCALI domain, which is decidedly unusual. Another warning sign is that, in order to confirm the process, the user is asked to enter their account details via a link sent by email.
Anyone who, unfortunately, clicks on the
REACTIVATE NOW link will be redirected to a suspicious web page, which has already been flagged as a deceptive page/website, as it is run by cybercriminals whose aim is to gain access to your most valuable data in order to use it for their own purposes.
To conclude, we urge you always to pay attention to every detail, however trivial, not to rush, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to the cybercriminals behind the scam, who will use them for illegal purposes.
17 June 2026 ==> Phishing Aruba - Final notice
SUBJECT: <
Final Notice: Imminent Suspension>
Below, we analyse another phishing attempt that purports to be a message from the
Aruba brand.
The message informs the recipient: ‘
The invoice due on 10 June 2026 has not yet been paid. If payment is not made by 18 June 2026, the service will be suspended and cannot be reactivated until the outstanding amount has been settled.’ It then invites them to make the payment in order to continue using the services hosted on
Aruba, via the following link:
Bring your subscription up to date
We should always be wary of requests to enter personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company
Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We can see straight away that the email address from which the message originates, <
support[at]maracujalia[dot]com>, is not associated with the official
Aruba domain. This is highly unusual and should certainly raise our suspicions.
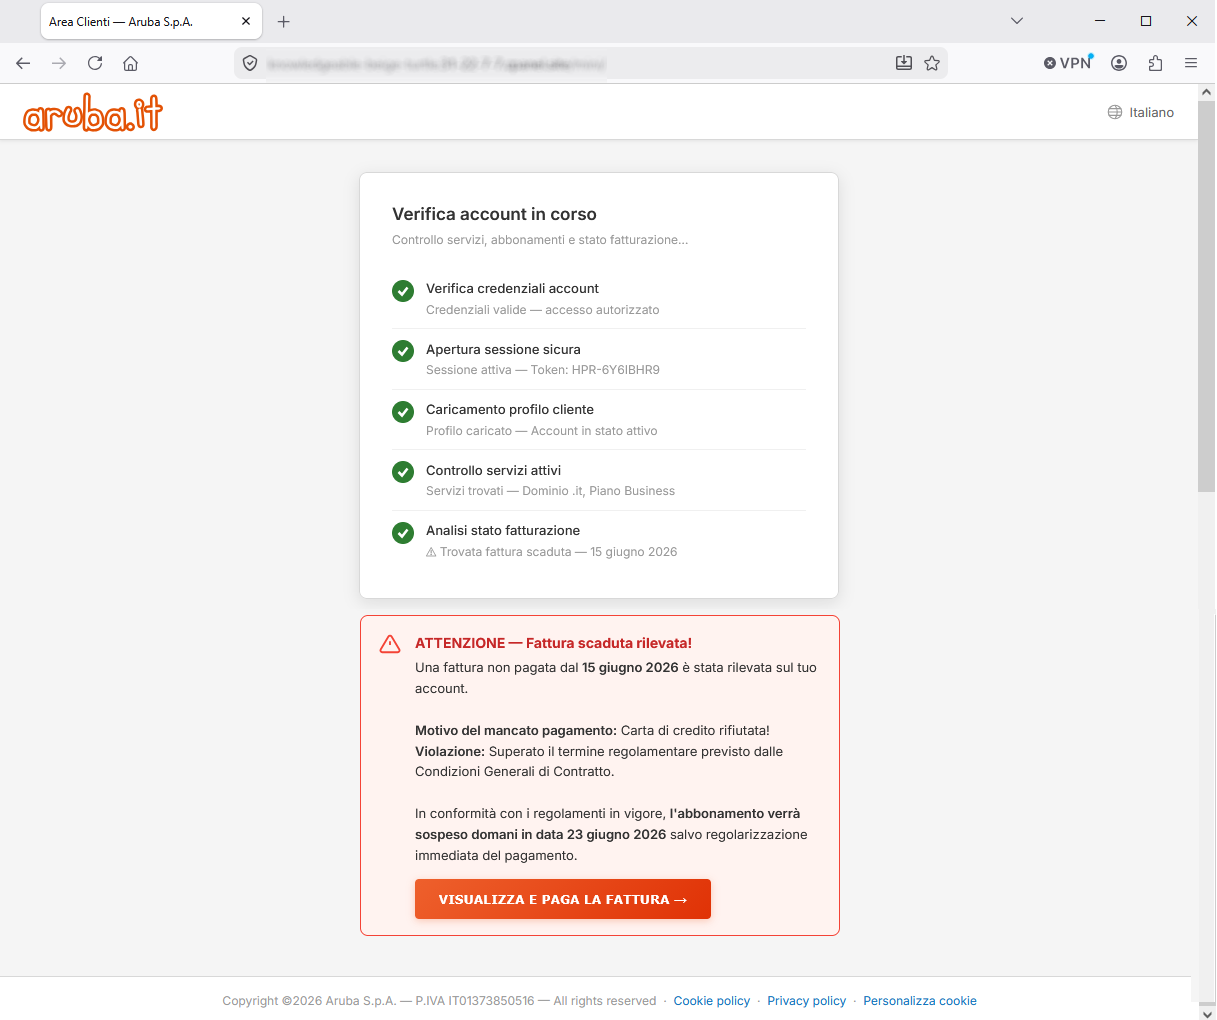
Anyone who unfortunately clicks on the
Bring your subscription up to date link will be redirected to a web page which, although it visually mimics the
Aruba account login page – as evidenced by the presence of the well-known company’s logo – has an unusual address/domain:
https[:]//[FakeDomainName*]
This page prompts the user to sign in to their customer area using their email username and password. The cybercriminals responsible for this scam are clearly trying to gain possession of these credentials.
Therefore, always pay the utmost attention, and always access the site only through the official pages, not via suspicious links.
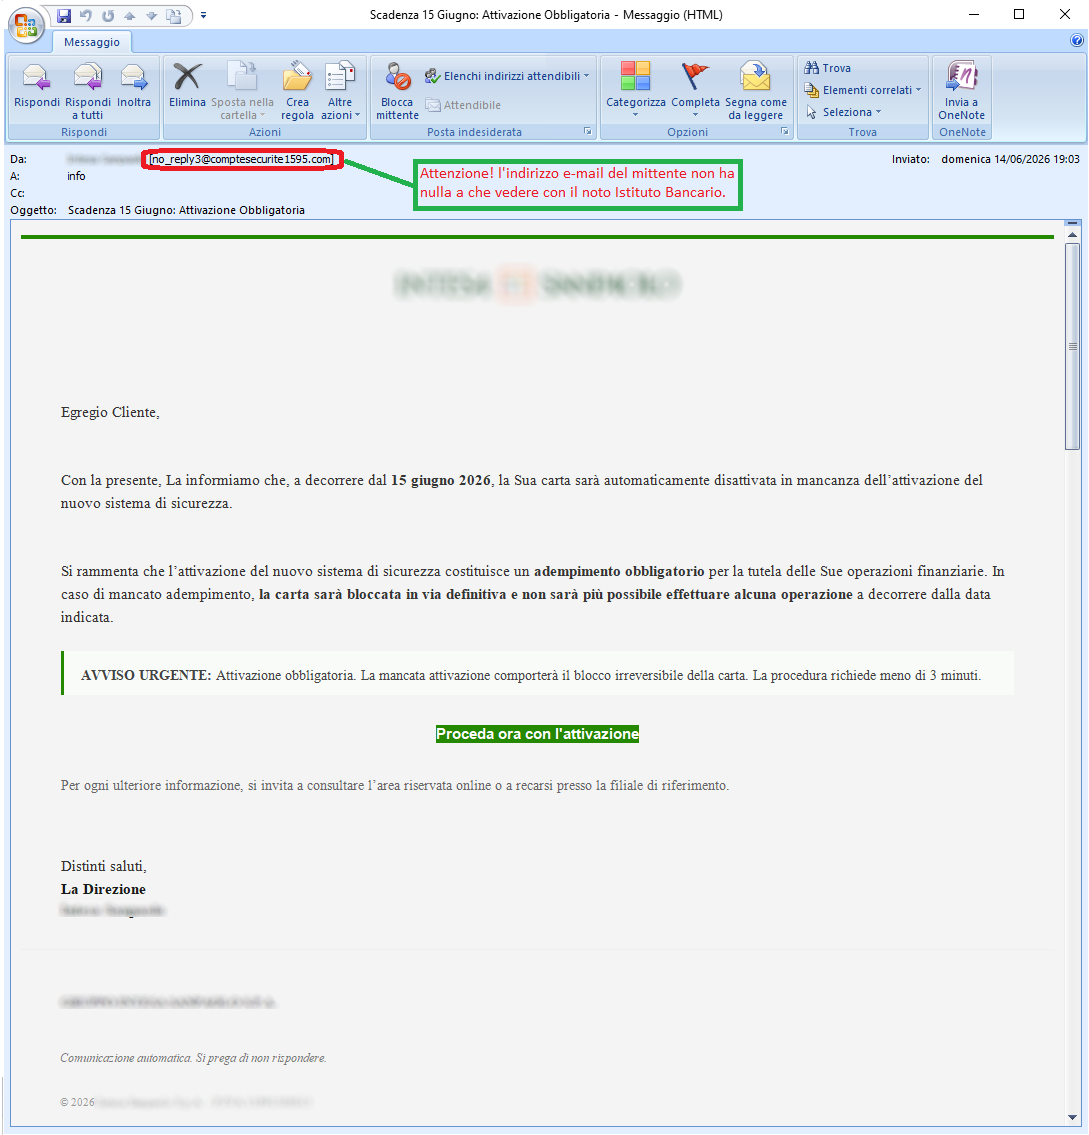
14 June 2026 ==> Phishing Bank
SUBJECT: <
Deadline 15 June: Mandatory activation>
The message, using graphics stolen from or similar to those of a well-known bank, attempts to pass itself off as an official communication in order to induce the recipient to comply with the request and fall into this trap based on social engineering technique.
It informs the unsuspecting recipient that, for security reasons, they must activate the new web security system by
15 June 2026. After the specified date, “
the card will be permanently blocked and it will no longer be possible to carry out any transactions”. Activation is mandatory to avoid any restrictions on the use of the card; the procedure is quick and easy the users just need to click on the following link:
Proceed now with the activation
We can see straight away that the alert message comes from a highly suspicious email address, <
no_reply3(at)comptesecurite1595(dot)com>, and contains very generic text, even though the cybercriminal has included the bank’s logo in an attempt to deceive the user. The aim is to trick the victim into logging into their banking app so that their details can be stolen.
Anyone who, unfortunately, clicks on the
Proceed now with the activation link will be redirected to a suspicious web page, which has already been flagged as a SCAM PAGE/SITE. Actually it is run by cybercriminals whose aim is to gain access to your most valuable data so that they can use it for their own purposes.
To conclude, we would urge you to always be wary of any email asking you to enter confidential information, and to avoid clicking on suspicious links, which could lead to a fake website that is difficult to distinguish from the original one.
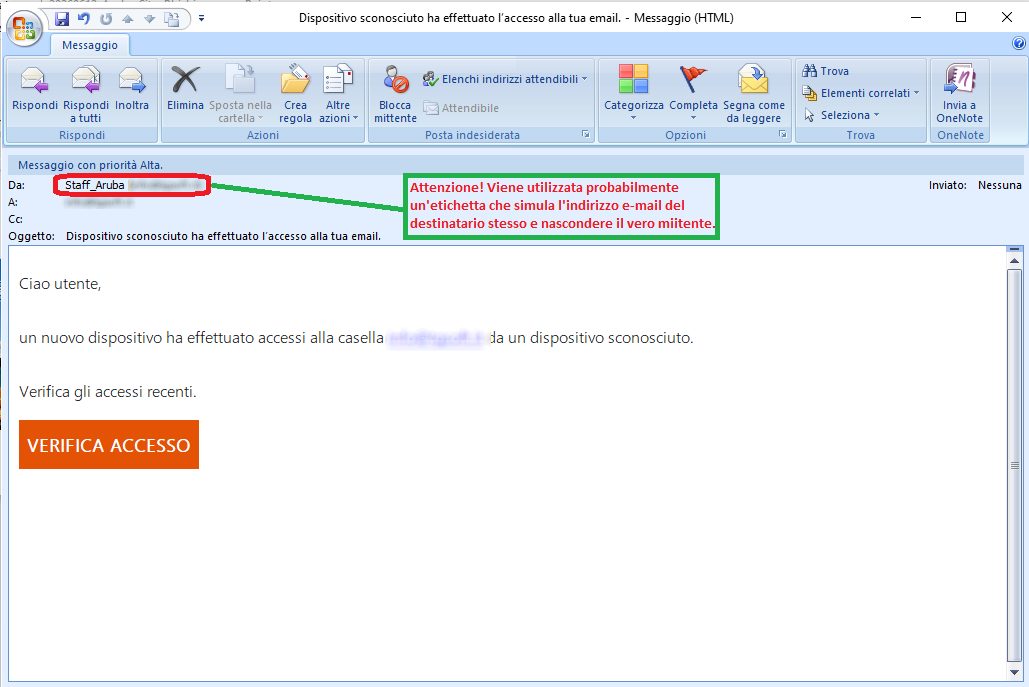
12 June 2026 ==> Phishing Aruba - Log in from a new device
SUBJECT: <
Unknown device has accessed your email.>
Here is another phishing attempt posing as a message from the
Aruba brand.
The message informs the recipient that a new, unknown device has accessed their email account. It then asks them to check their login history and look out for any irregularities via the following link:
CHECK ACCESS
We should always be wary of requests to enter personal details via suspicious links sent by email.
The well-known web hosting, email and domain registration company,
Aruba, is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We immediately see that the email address of the message does not belong to the official
Aruba domain, but is likely using a label that mimics the recipient’s email address. This is highly unusual and should certainly raise our suspicions.
Anyone who unfortunately clicks on the
CHECK ACCESS link will be redirected to a web page which, although it visually mimics the
Aruba account login page – as evidenced by the presence of the well-known company’s logo – has an unusual address/domain:
https[:]//[FakeDomainName*]
On this page, users are asked to log in to their customer account by entering their email address and password. The aim of the cybercriminals behind the scam is, in fact, clearly to steal these details.
Therefore, always pay close attention and only access the site via the official pages, not via suspicious links.
12 June 2026 ==> Phishing Email Account
SUBJECT: <
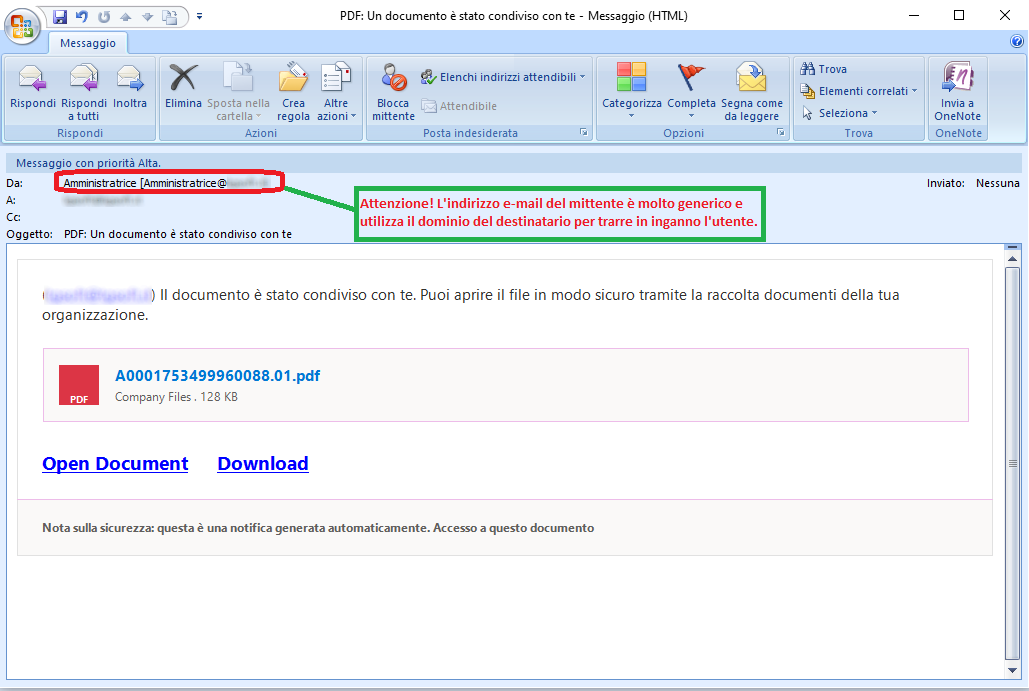
PDF: A document has been shared with you>
Below, we analyse the phishing attempt, which aims to steal the victim’s email account credentials.
The message states: ‘
The document has been shared with you. You can open the file securely via your organisation’s document library.’ . No other information is provided apart from the name of the shared file, '
A0001753499960088.01.pdf'. To continue, the user must download or open the document via the following link:
Open Document o Download
When we examine the message we see that it has an email address <
amministratrice(at)*******>, which seems to come from the recipient’s own email domain. This is highly unusual and should certainly raise our suspicions.
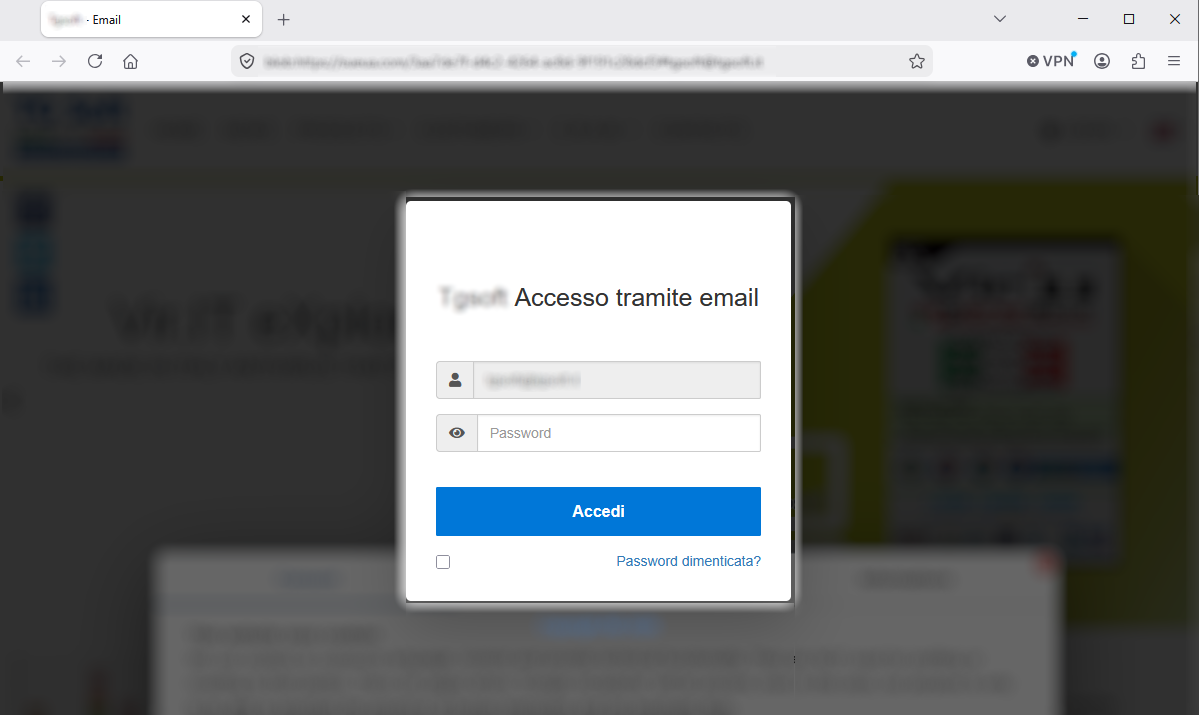
Anyone who unfortunately clicks on the links provided will be redirected to a fraudulent web page that mimics the email account login page.
On this page, the user is asked to log in to their account by entering, amongst other things, their email password in order to download the received document.
Actually, the page to which the user is redirected to enter their email account credentials is hosted on a suspicious address/domain, which is listed below:
https[:]//[FakeDomainName*]
We urge you to always pay attention to every detail, however trivial, and not to enter your personal details and/or passwords into forms hosted on fake websites, as these will be sent to a remote server and used by cybercriminals, with all the associated risks that one can easily imagine.
08 June 2026 ==> Phishing PagoPA
SUBJECT: <
Payment notice>
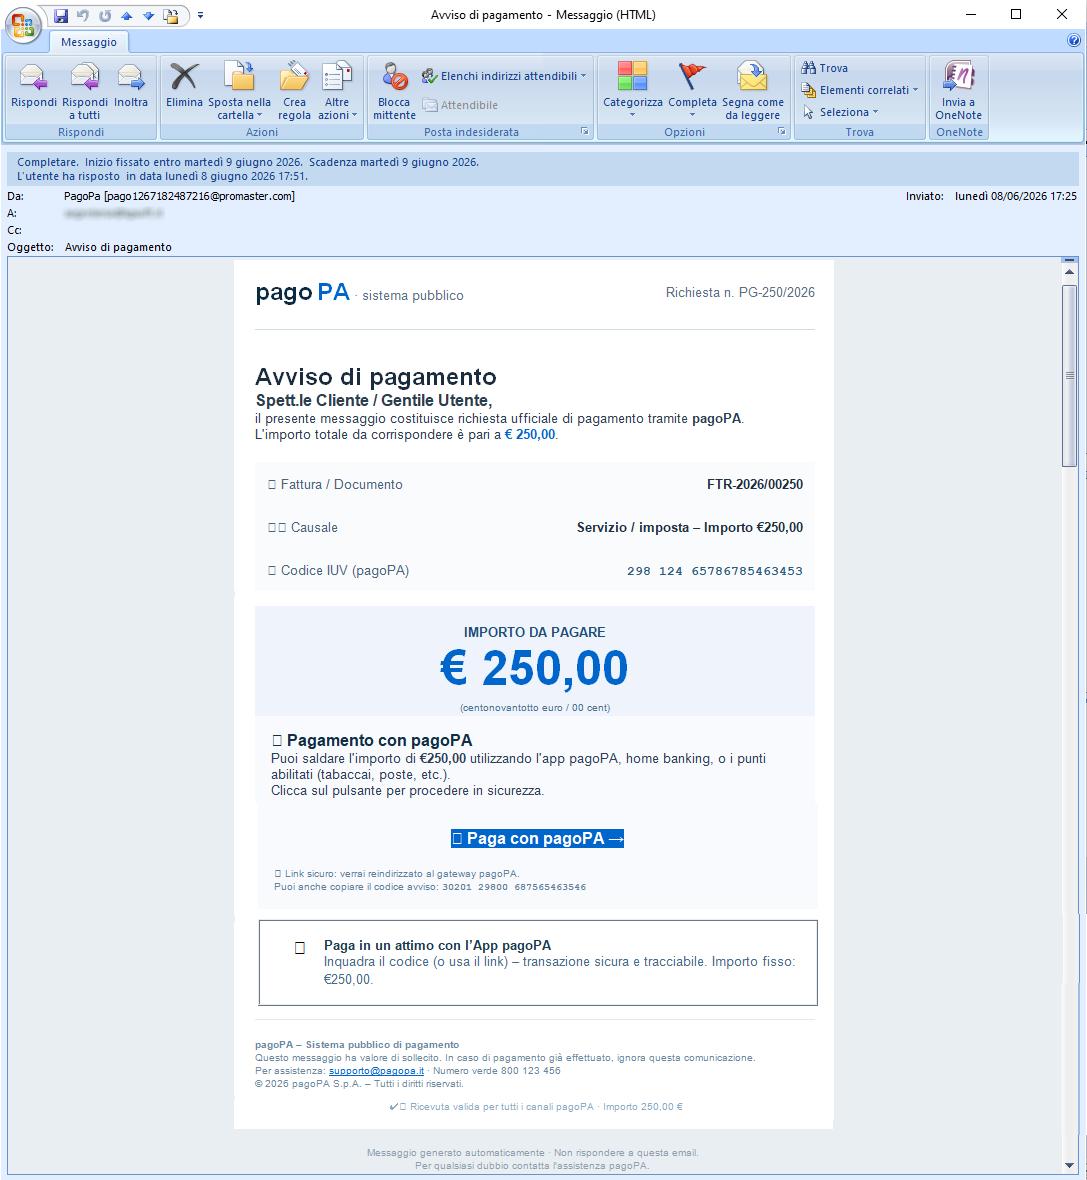
This month, we’re analysing the following phishing attempt, which purports to be a message from
PagoPA, the well-known payment system used by public administrations and public service providers in Italy.
The message notifies the recipient of a general payment notice, which contains a reference number: <
Request No. PG-250/2026>.
The amount for the service/tax is then shown as
€ 250.00. The user is then asked to make the payment via the link below:
Pay via pagoPA
The well-known digital payment platform is, of course, in no way involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal the unsuspecting recipient’s sensitive data.
On closer inspection of the message, there are a number of clues that should raise our suspicions. We immediately observe that the email address <
pago1267182487216[at]promaster[dot]com> does not belong to the official
PagoPA domain. This is highly unusual and should certainly raise our suspicions.
Anyone who unfortunately clicks on the
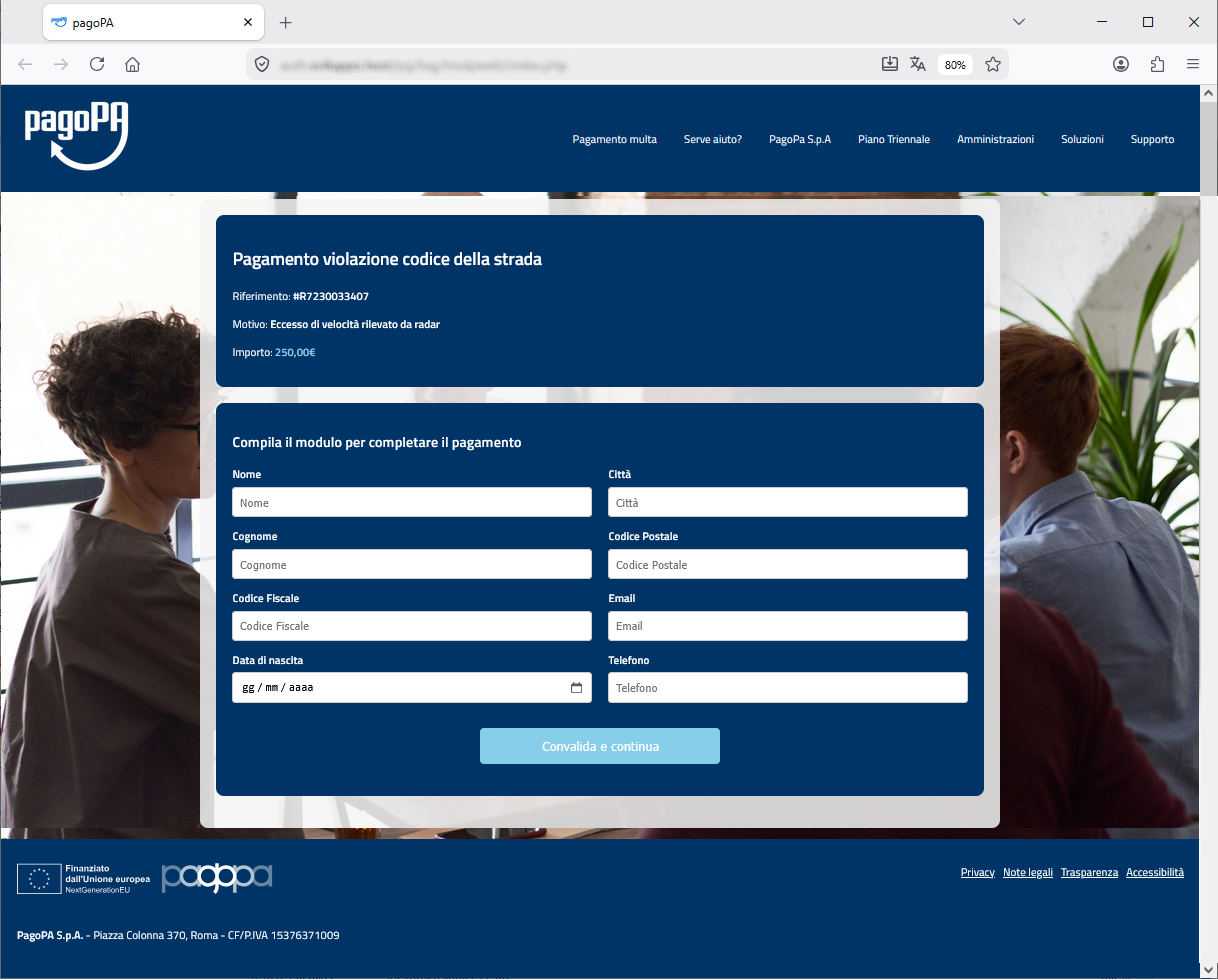
Pay via pagoPA link will be redirected to a web page which, as we can see from the image on the side, is well designed and mimics the official
PagoPA website quite closely.
We can see, however, that the landing page in this case is hosted at the URL:
https[:]//[FakeDomainName*]/... which is completely unrelated to the official
PagoPA website.
We urge you to always pay attention to even the smallest details and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to a remote server and used by cybercriminals.
02 June 2026 ==> Phishing Banco BPM
SUBJECT: <
BPM.it Announcement>
Below we examine a phishing campaign carried out through an email that uses branding stolen from, or resembling, that of a well-known national bank — in this case,
BANCO BPM — in an attempt to appear as an official communication and trick unsuspecting recipients into following its instructions and falling victim to this social engineering scam.
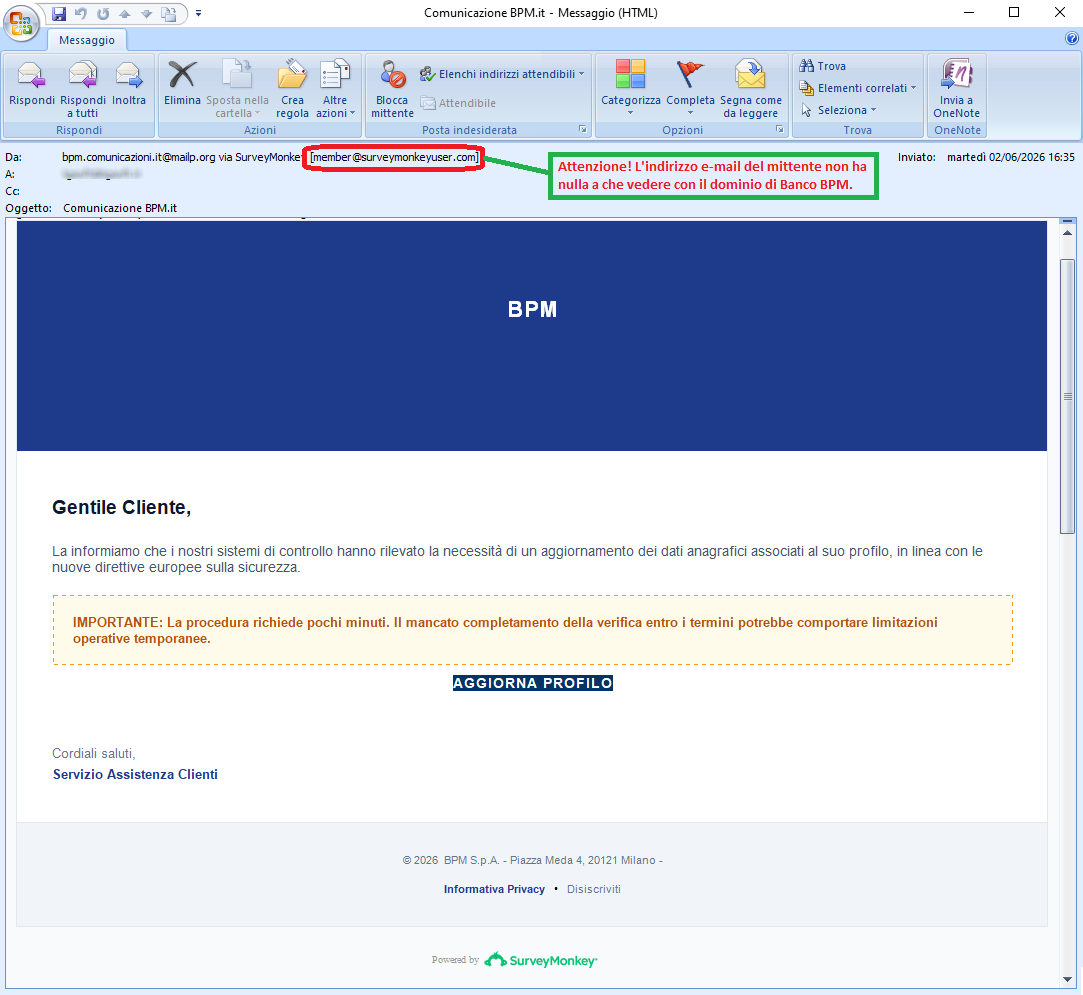
The message informs the recipient: ‘Our monitoring systems have identified the need to update the personal details associated with your profile, in line with the new European security directives.’ They are then asked to update their details by clicking on the following link:
UPDATE PROFILE
We can see straight away that the alert message comes from a highly suspicious email address, <member(at)surveymonkeyuser(dot)com>, and contains very generic text, although the cybercriminal has been careful enough to include the registered office of BANCO BPM at the bottom, which could mislead the user.
The aim is to trick the victim into logging in to their online banking account.
Anyone who unfortunately clicks on the UPDATE PROFILE link will be taken to a suspicious website unrelated to the official BANCO BPM domain. The page has already been flagged as a deceptive/scam website, managed by cybercriminals seeking to steal sensitive personal information for malicious purposes.
To conclude, we urge you to always be wary of any email asking you to enter confidential information, and to avoid clicking on suspicious links that could lead you to a fake website difficult to distinguish from the original one.
02 June 2026 ==> Phishing Aruba - Non-payment
SUBJECT: <
URGENT – Scheduled Disconnection due to Non-payment>
Below, we analyse another phishing attempt that purports to be a message from the
Aruba brand.
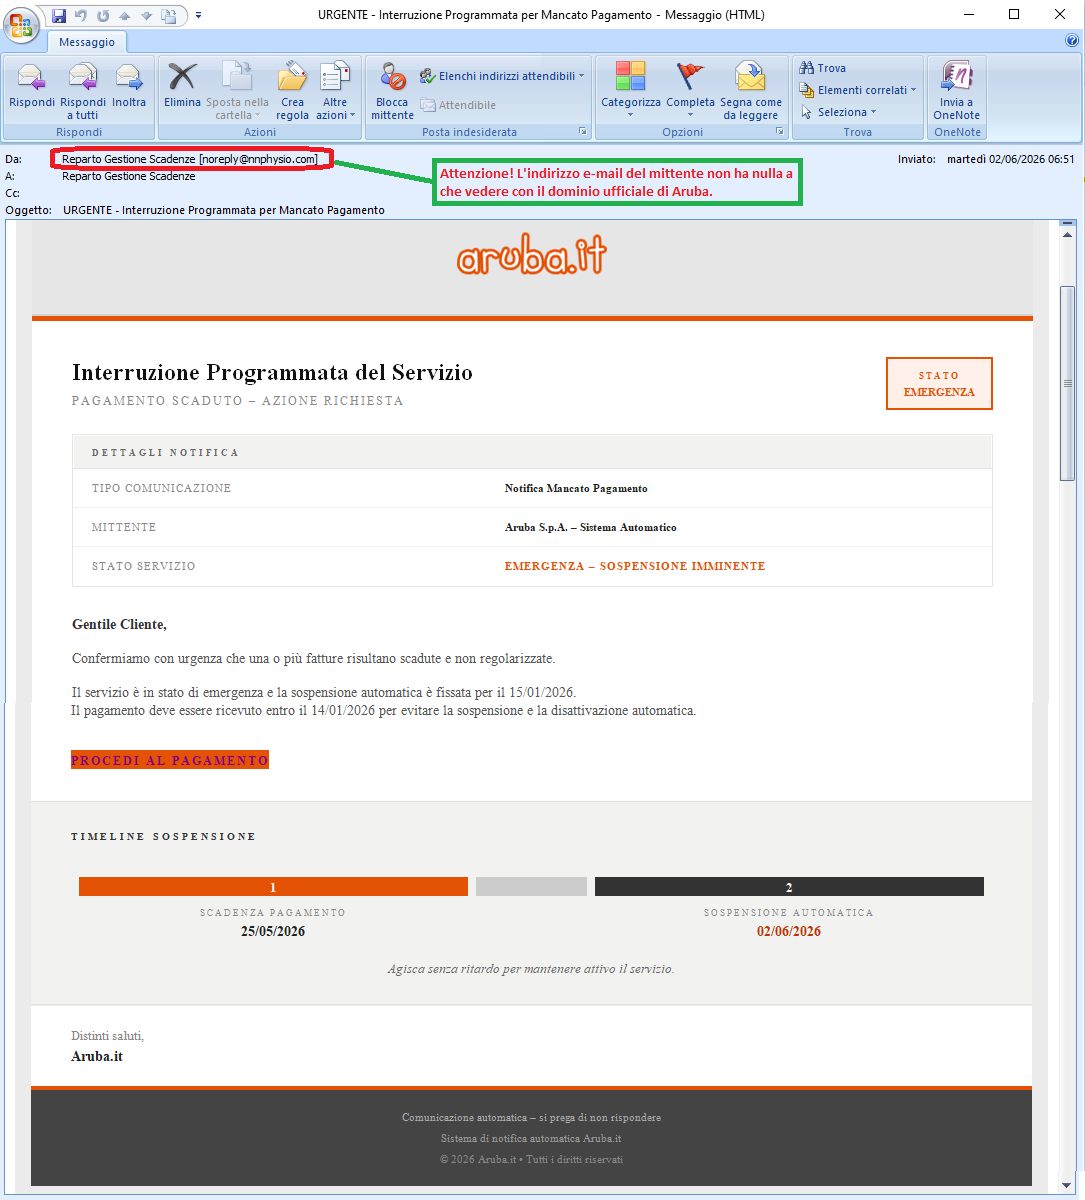
The message informs the recipient that the service will be suspended due to non-payment. It reads: ‘
We urgently confirm that one or more invoices are overdue and have not been settled. The service is in a state of emergency and automatic suspension is scheduled for 15 January 2026. Payment must be received by 14 January 2026 to avoid suspension and automatic deactivation.’ It then asks them to make the payment in order to continue using the services hosted on
Aruba, via the following link:
PROCEED TO PAYMENT
We can see straight away that there is an inconsistency with the dates, as the email refers to a service suspension scheduled for
15 January 2026, whilst the email arrived on
2 June 2026. Let's always exercise caution when we're asked to enter our personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company,
Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We can see straight away that the email address from which the message originates, <
no-reply[at]nnphysio[dot]com>, is not associated with the official
Aruba domain. This is highly unusual and should certainly raise our suspicions.
Anyone who unfortunately clicks on the
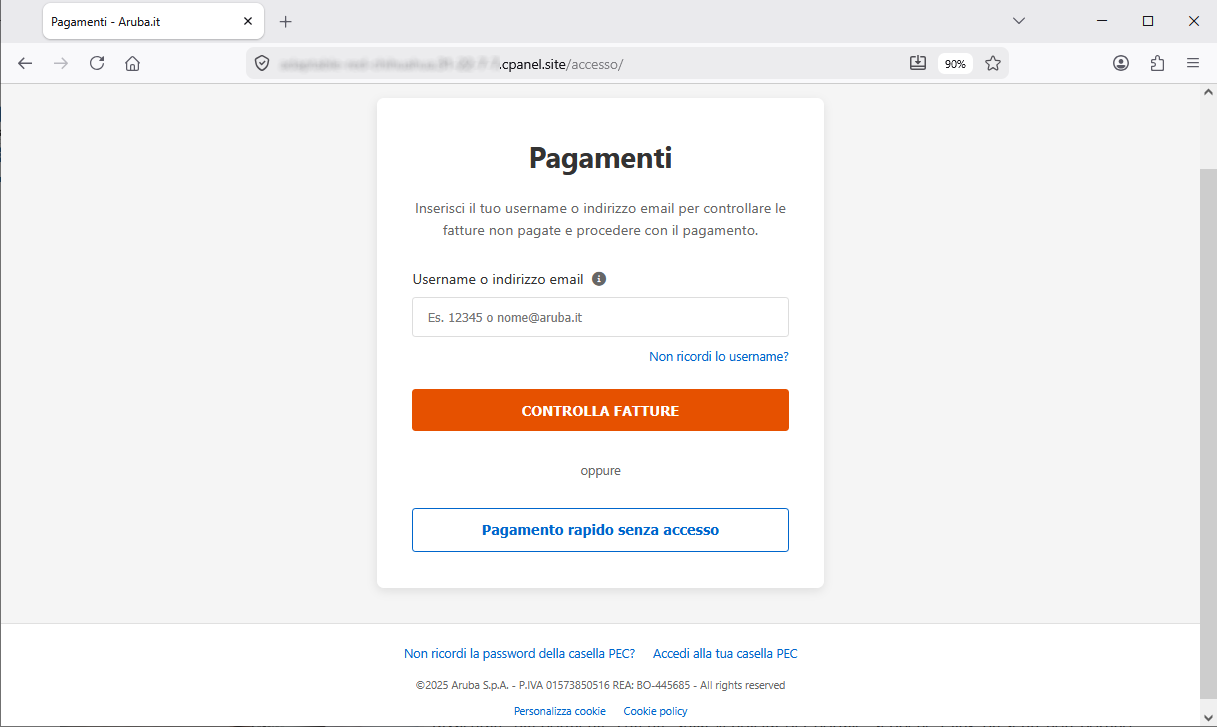
PROCEED TO PAYMENT link will be redirected to a web page which, although it visually mimics the
Aruba account login page – as evidenced by the presence of the well-known company’s logo – has an unusual address/domain:
https[:]//[FakeDomainName*]
On this page, the user is asked to log in to their customer account by entering their email address, username and password. The aim of the cybercriminals behind the scam is, in fact, clearly to gain hold of these details.
Therefore, always exercise the utmost caution and access your accounts only through official pages, never via suspicious links.
01 June 2026 ==> Phishing Aruba - Unpaid invoice
SUBJECT: <
Unpaid invoice>
Phishing attempts posing as communications from the
Aruba brand are continuing this month.
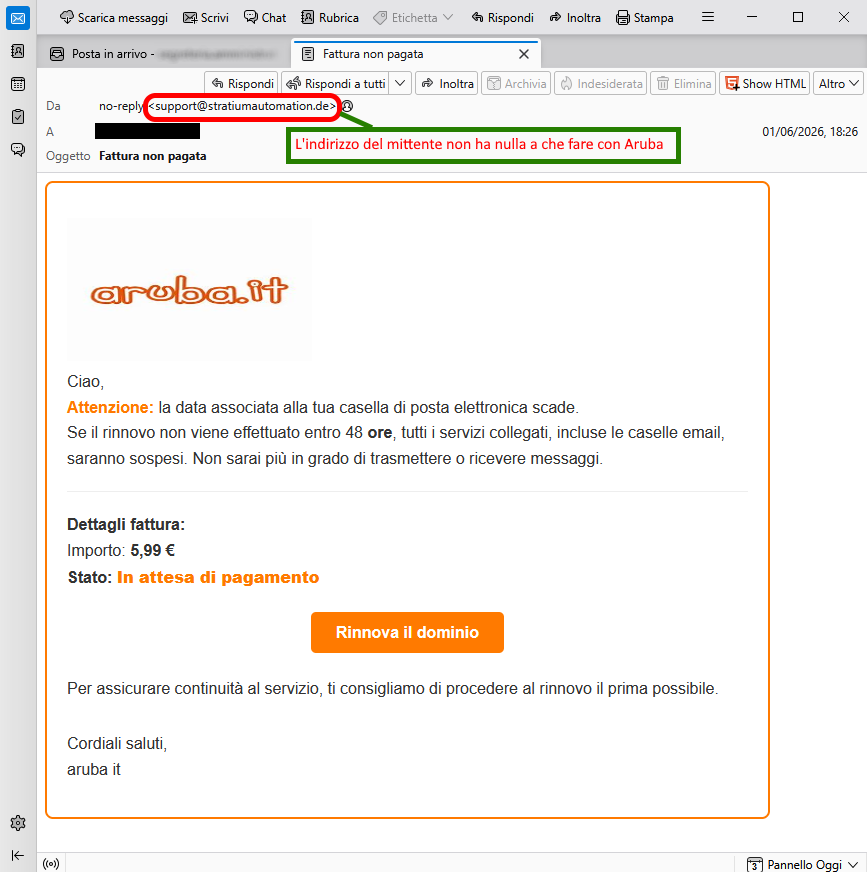
This message informs the recipient that their domain hosted on
Aruba is due to expire. It therefore warns them that, to avoid service interruptions, incoming emails being blocked or the loss of the domain, they must renew it within
48 hours; otherwise, they will no longer be able to send or receive messages. To renew, they simply need to click on the following link:
Renew your domain
Let's always exercise caution when we're asked to enter our personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company
Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We see straight away that the email address from which the message originates, <
support[at]stratiumautomation[dot]de>, is not associated with the official
Aruba domain. This is highly unusual and should certainly raise our suspicions.
Anyone who unfortunately clicks on the
Renew your domain link will be redirected to a fraudulent webpage, that has already been reported as a phishing site. It is in fact run by cybercriminals whose aim is to gain access to your most valuable data so they can use it for their own purposes.
We urge you to always pay attention to every detail, however trivial, not to rush, and not to enter your personal details and/or passwords into forms hosted on fake websites.
01 June 2026 ==> Phishing DHL
SUBJECT:
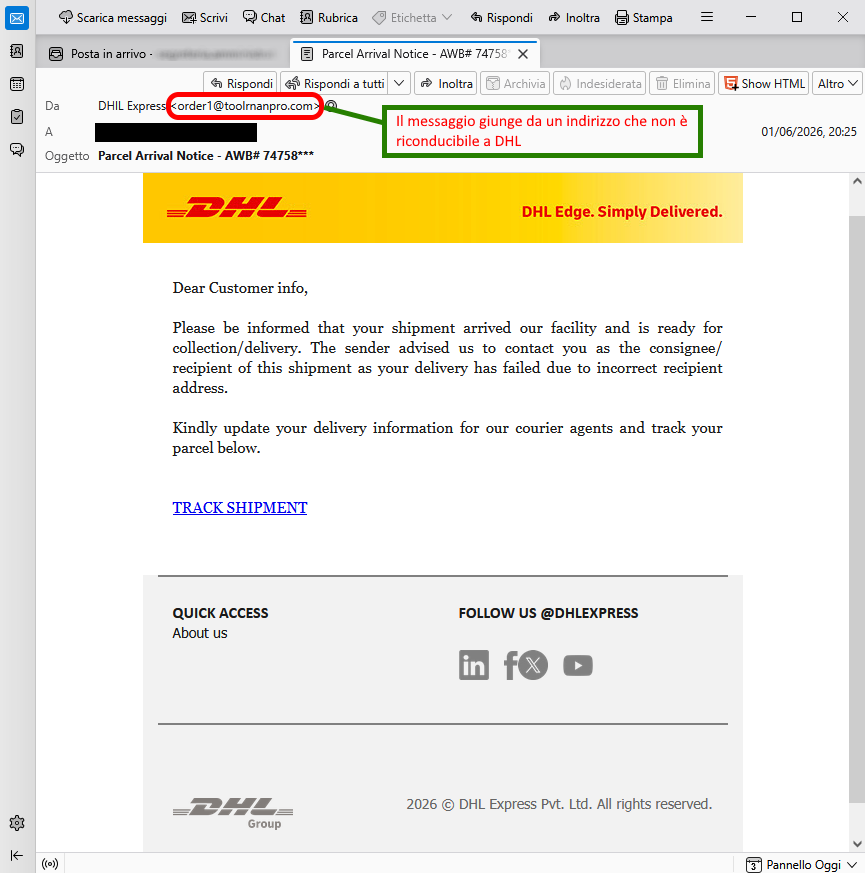
< Parcel Arrival Notice - AWB# 74758*** >
Below is a new phishing attempt, disguised as a fake message from the courier
DHL regarding the delivery of a supposed parcel.
The message, in English, informs the unsuspecting recipient that their parcel is on hold. It states: ‘
We would like to inform you that your parcel has arrived at our premises and is ready for collection/delivery. The sender has asked us to contact you, as the recipient of the parcel, since delivery was unsuccessful due to an incorrect delivery address.’
These messages are increasingly being used to carry out scams targeting consumers who are turning to e-commerce more and more for their purchases.
To proceed with the delivery, the user must click on the following link:
TRACK SHIPMENT
The email comes from an email address <
oredr1(at)toolrnanpro(dot)com> unrelated to the
DHL. domain. This is highly unusual and should certainly raise our suspicions. Anyone who clicks on the links will be redirected to a suspect web page.
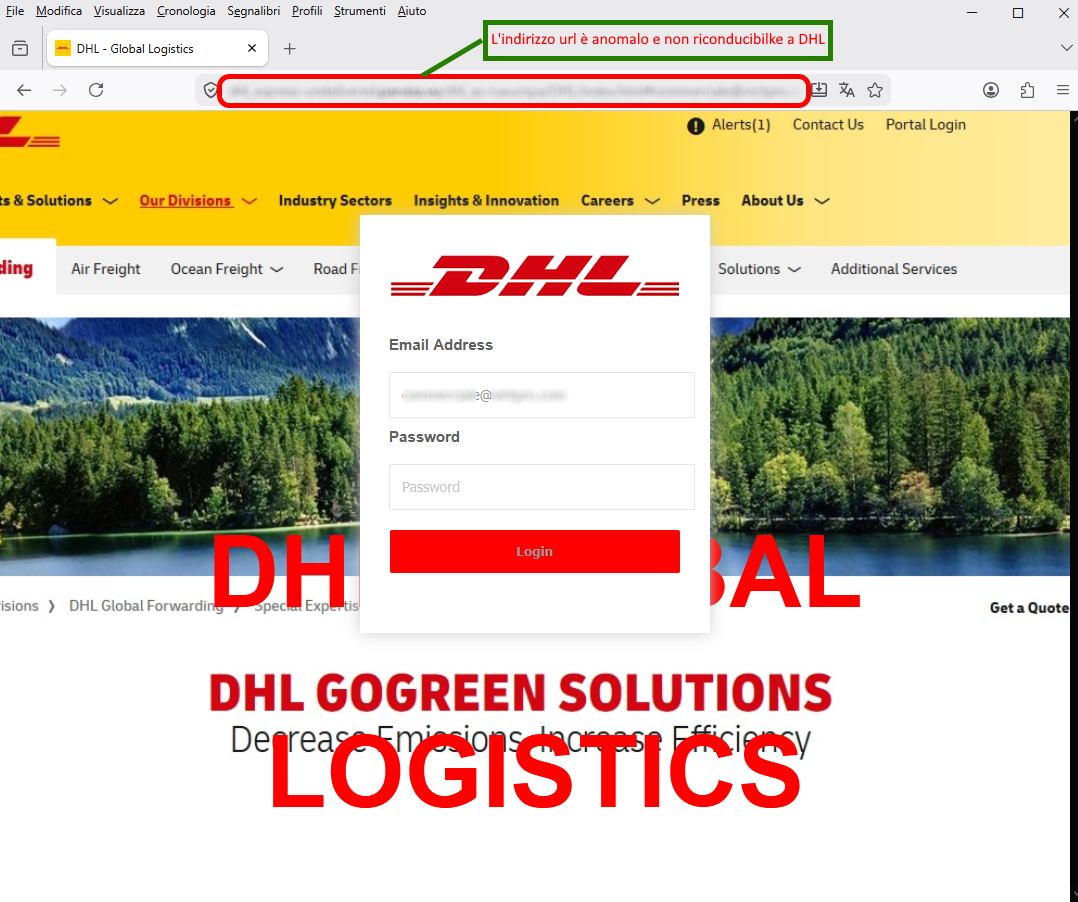
Although the landing page is visually misleading, it is hosted at a URL address unrelated to the official
DHL domain.
Here, the user is prompted to log in to their account by entering their password.
We can see that the URL displayed in the browser address bar is unusual and cannot be traced back to the official domain of the company.
https[:]//[FakeDomainName*]/....
If we enter data on fake websites, this information will be sent to the cybercriminals behind the scam, who will use it for illegal purposes. We therefore urge you not to rush and to pay close attention to every detail, however trivial it may seem.
A little attention and a quick glance can save you a lot of hassle and headaches...
We urge you NOT to be fooled by these types of e-mails, which, even though they use familiar and not particularly sophisticated approach techniques, if there is a resurgence, with reasonable likelihood more than a few unfortunates will be fooled.
We invite you to check the following information on phishing techniques for more details:
02/04/2026 11:01 - Phishing: the most common credential and/or data theft attempts in April 2026.
04/03/2026 10:44 - Phishing: the most common credential and/or data theft attempts in March 2026.
04/02/2026 10:33 - Phishing: the most common credential and/or data theft attempts in February 2026.
08/01/2026 09:53 - Phishing: the most common credential and/or data theft attempts in January 2026.
04/12/2025 15:56
- Phishing: the most common credential and/or data theft attempts in December 2025.
04/11/2025 14:45
- Phishing: the most common credential and/or data theft attempts in Novembre 2025.
01/10/2025 16:40 - Phishing: the most common credential and/or data theft attempts in October 2025.
04/09/2025 09:45 - Phishing: the most common credential and/or data theft attempts in September 2025.
05/08/2025 08:58- Phishing: the most common credential and/or data theft attempts in August 2025.
01/07/2025 16:04 - Phishing: the most common credential and/or data theft attempts in July 2025.
05/06/2025 09:22 - Phishing: the most common credential and/or data theft attempts in June 2025.
05/05/2025 15:03 - Phishing: the most common credential and/or data theft attempts in May 2025.
Try Vir.IT eXplorer Lite
 If you are not yet using Vir.IT eXplorer PRO, it is advisable to install Vir.IT eXplorer Lite -FREE Edition- to supplement the antivirus in use to increase the security of your computers, PCs and SERVERS.
Vir.IT eXplorer Lite has the following special features:
- freely usable in both private and corporate environments with Engine+Signature updates without time limitation;
- fully interoperable with other AntiVirus software and/or Internet Security products (both free and commercial) already installed on your computer. It doesn't need any uninstallation and it doesn't cause slowdowns, as some features have been appropriately reduced to ensure interoperability with the AntiVirus software already on your PC/Server. This, however, allows cross-checking through the scan;
- it identifies and, in many cases, even removes most of the viruses/malware actually circulating or, alternatively, allows them to be sent to the C.R.A.M. Anti-Malware Research Center for further analysis to update Vir.It eXplorer PRO;
- through Intrusion Detection technology, also made available in the Lite version of Vir.IT eXplorer, the software is able to report any new-generation viruses/malware that have set in automatically and send the reported files to TG Soft's C.R.A.M
- Download Vir.IT eXplorer Lite from the official distribution page of TG Soft's website.
Acknowledgements
TG Soft's Anti-Malware Research Center would like to thank all users, customers, reseller technicians, and all people who have transmitted/reported material attributable to Phishing activities to our Research Center, that allowed us to make this information as complete as possible.
How to submit suspicious emails for analysis as possible phishing but also virus/malware or Crypto-Malware
You can submit materials to TG Soft's Anti-Malware Research Center safely and free of charge in two ways:
- any suspect email can be sent directly by the recipient's e-mail, to the following mail lite@virit.com,choosing as sending mode "Forward as Attachment" and inserting in the subject section "Possible phishing page to verify" rather than "Possible Malware to verify";
- save the e-mail to be sent to TG Soft's C.R.A.M. for analysis as an external file to the e-mail program used. The resulting file must be sent by uploading it from the page Send Suspicious Files (http://www.tgsoft.it/italy/file_sospetti.asp). Obviously if you want a feedback on the analysis of the data submitted, you have to indicate an e-mail address and a brief description of the reason for the submission (for example: possiible / probable phishing; possible / probable malware or other).
For more details on how to safely forward suspicious e-mails, we invite you to consult the following public page:
How to send suspicious emails for analysis
We provide all this information to help you prevent credential theft, viruses/malware or, even worse, next-generation Ransomware / Crypto-Malware.
TG Soft Anti-Malware Research Centre (C.R.A.M.)