PHISHING INDEX
Below are the most common email phishing attempts detected by the TG Soft Anti-Malware Research Center in
AUGUST 2026:
19/08/2026 =>
Klarna
19/08/2026 =>
Email Account
12/08/2026 =>
Webmail
12/08/2026 =>
Email Account
10/08/2026 =>
DHL
09/08/2026 =>
GLS
06/08/2026 =>
Netflix
05/08/2026 =>
Bank
04/08/2026 =>
Aruba
01/08/2026 =>
Webmail
These emails aim to deceive unsuspecting victims into providing sensitive information, such as bank account details, credit card codes, or personal login credentials, with all the easily imaginable consequences.
19 August 2026 ==> Phishing Klarna
SUBJECT: <
Email verification requested>
This month, we’re examining a new phishing attempt that pretends to be a message from
Klarna, the Swedish payment service.
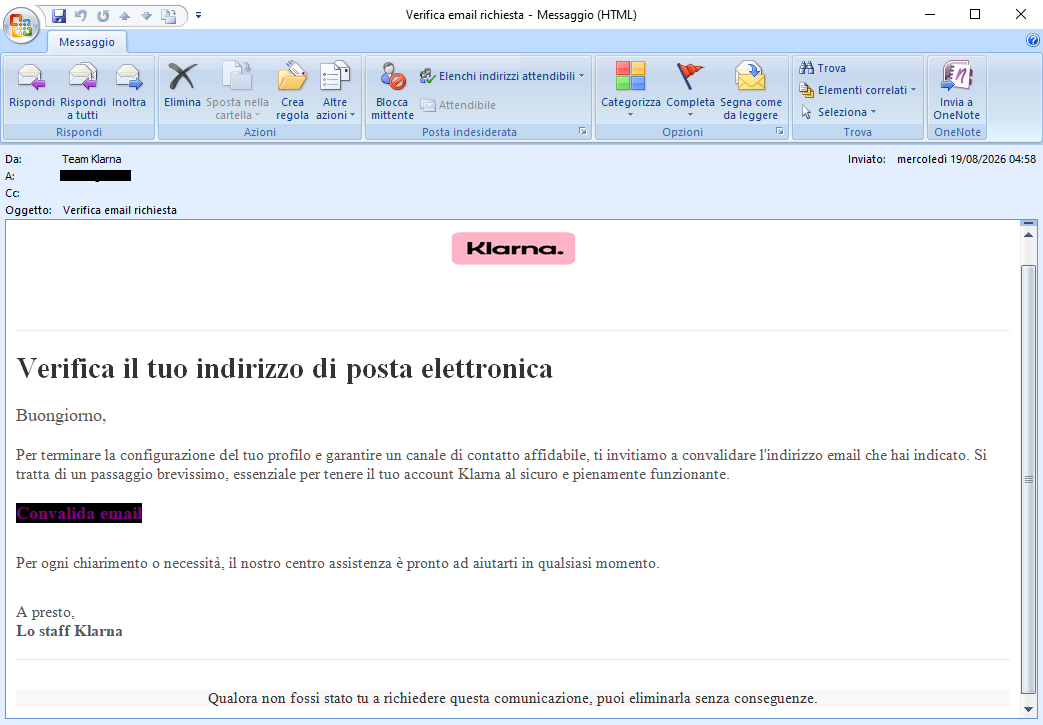
The message informs the recipient: “
To complete your profile setup and ensure a reliable means of contact, please verify the email address you have provided.”
It then asks them to complete this step to enhance the security of their account via the following link:
Email verification
The well-known online payment company
Klarna is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from the unsuspecting recipient.
When we examine the message closely, there are a few clues that should raise our suspicions. In fact, the email address of the message cannot be traced back to the official
Klarna domain, a highly unusual circumstance that should make us wary.
Anyone who unfortunately clicks on the
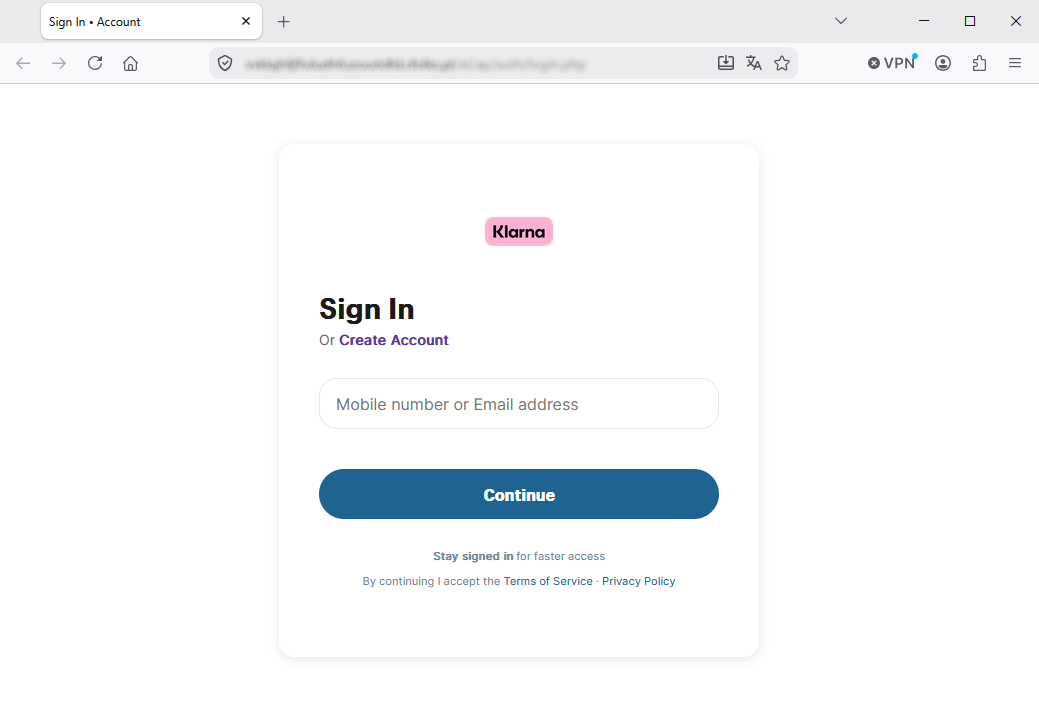
Email verification link will be redirected to a web page which, although it visually mimics the
Klarna account login page, has an anomalous address/domain:
https[:]//[FakeDomainName*]
On this page, users are invited to log in to their customer area by entering the username and password for their email account, from where they can then retrieve their messages before they are deleted.
We always urge you to pay attention to every detail, however trivial, not to rush, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to the cybercriminals behind the scam, who will use them for illegal purposes.
19 August 2026 ==> Phishing Email Account
SUBJECT: <
Final Notice: ******* Account Status Confirmation Required ****** 11:15 PM>
Below, we examine another phishing attempt aimed at stealing the victim’s email account credentials.
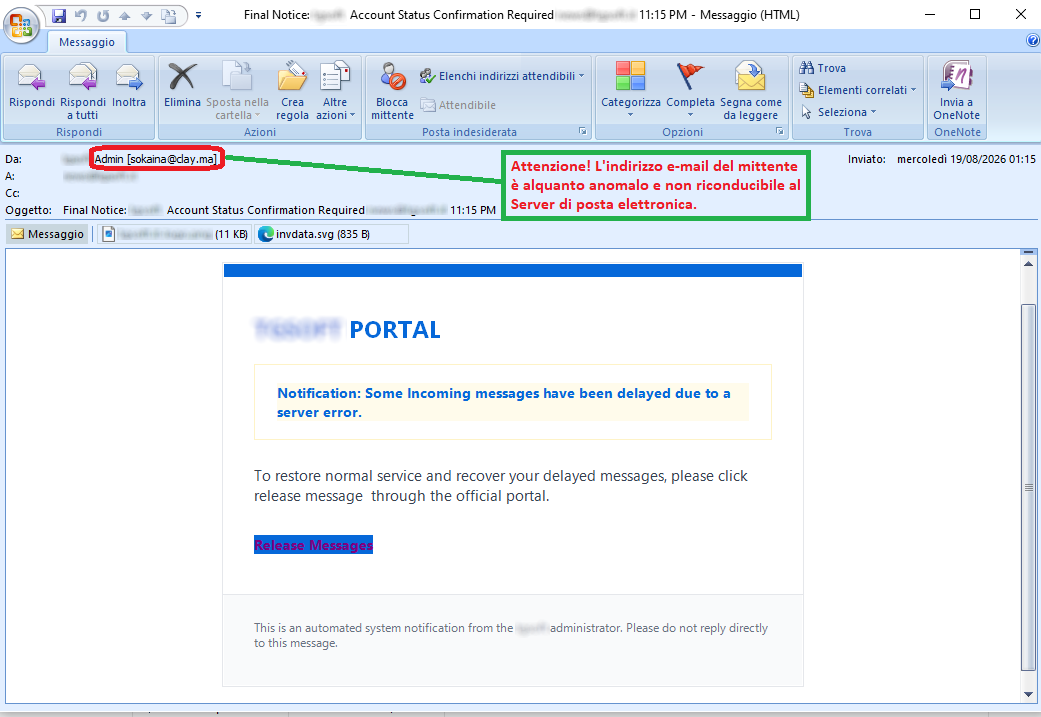
The message, in English, informs the recipient that, due to a server error, some incoming messages have been delayed. To restore normal service and retrieve the delayed messages, the user must click on the following link:
Release Messages
When we examine the message, we see that it contains a rather unusual email address that does not belong to the recipient’s email domain: <
sokaina(at)clay(dot)ma>. This is decidedly unusual and should certainly arouse our suspicion.
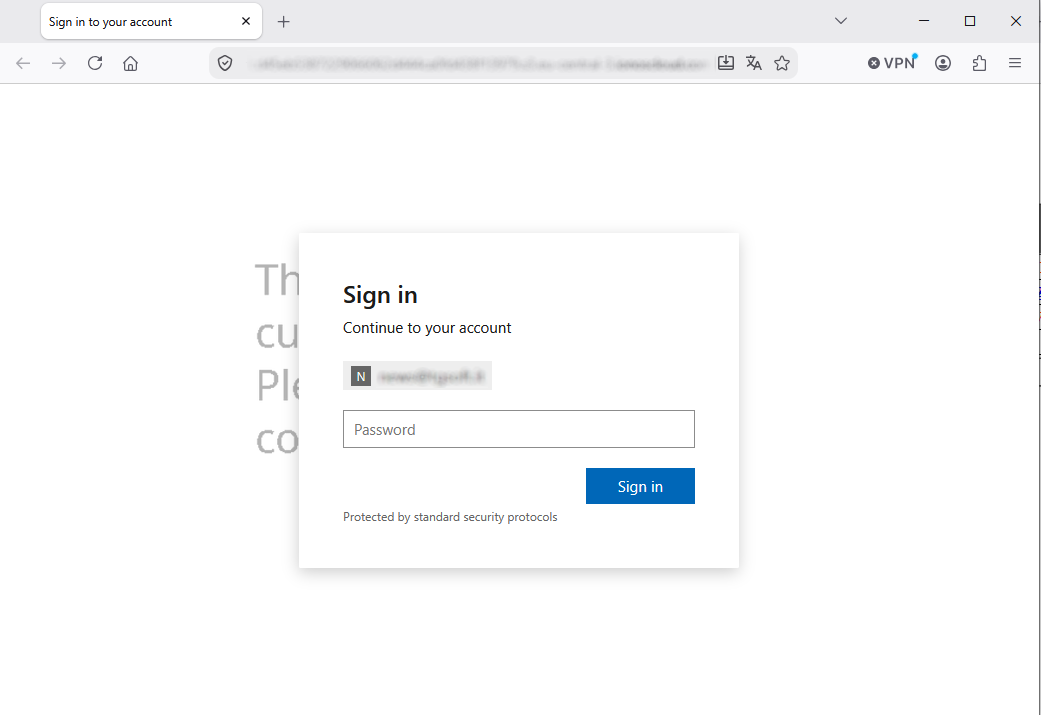
Anyone who unfortunately clicks on the link provided will be redirected to a fraudulent web page, which is designed to look like the email account login page.
This page prompts the user to sign in by entering their email password, supposedly to retrieve pending messages.
Actually, the page where the user is redirected to enter their email account credentials is hosted on a suspicious address/domain:
https[:]//[FakeDomainName*]
We always urge you to pay attention to every detail, however trivial, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to a remote server and used by cybercriminals, with all the associated risks easily imaginable.
12 August 2026 ==> Phishing Webmail
SUBJECT: <
***** mails have been put on hold in the email server database.>
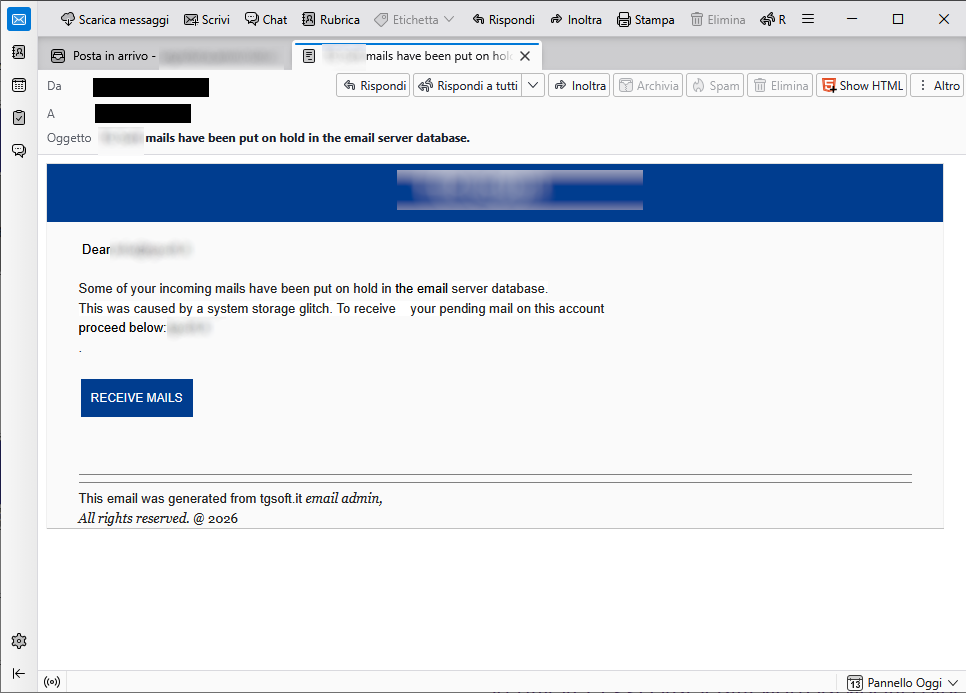
Below, we examine the phishing attempt, which aims to steal the victim’s email account credentials.
The message, in English, warns the recipient: “
Some of the incoming messages have been held up in the mail server’s database. This problem was caused by a fault in the system archive.” To receive the messages held up on this account, the user must click on the following link:
RECEIVE MAILS
Looking at the message, we see that it contains an email address created specifically using the recipient's email domain: <IT(at)*******>. This is highly unusual and should certainly raise our suspicions.
Anyone who, unfortunately, clicks on the
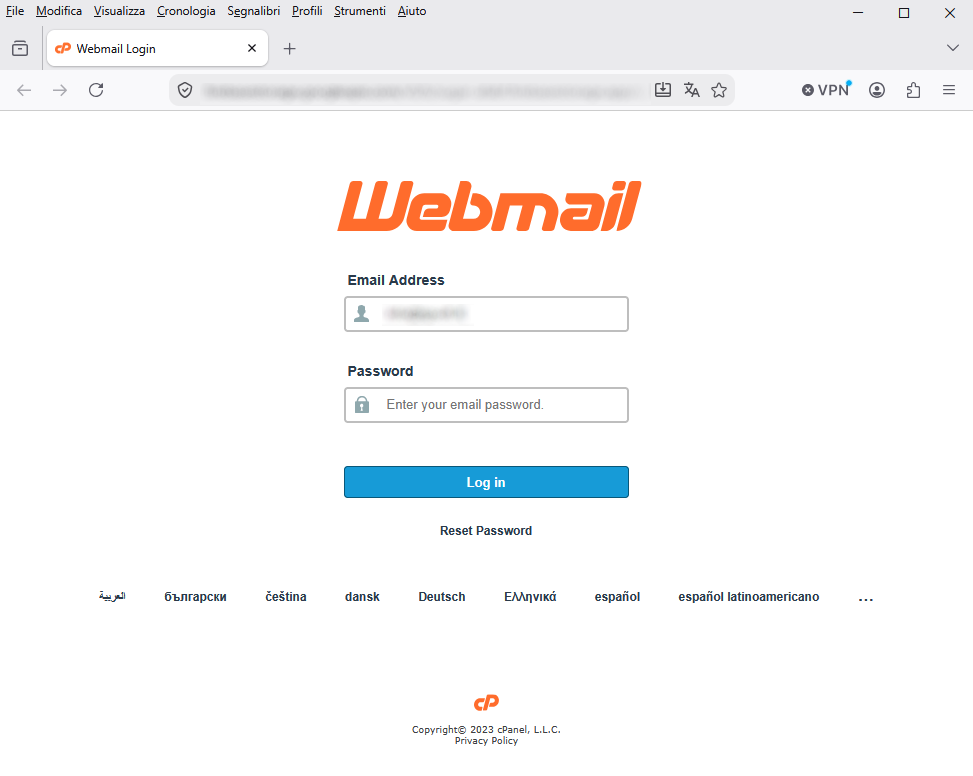
RECEIVE MAILS link will be redirected to a fraudulent web page, which is designed to look like the email account login page.
This page prompts the user to access their account by providing, specifically, their email account password to update their details.
Actually, the page where the user is redirected to enter their email account credentials is hosted on a suspicious address/domain, which is as follows:
https[:]//[FakeDomainName*]
We always urge you to pay attention to every detail, however trivial, and never enter personal information or passwords into forms hosted on fake websites. Such data may be sent to a remote server and used by cybercriminals, with all the risks this entails.
12 August 2026 ==> Phishing Email Account
SUBJECT: <
Password xxx.com" Error: xxxx@xxx.com>
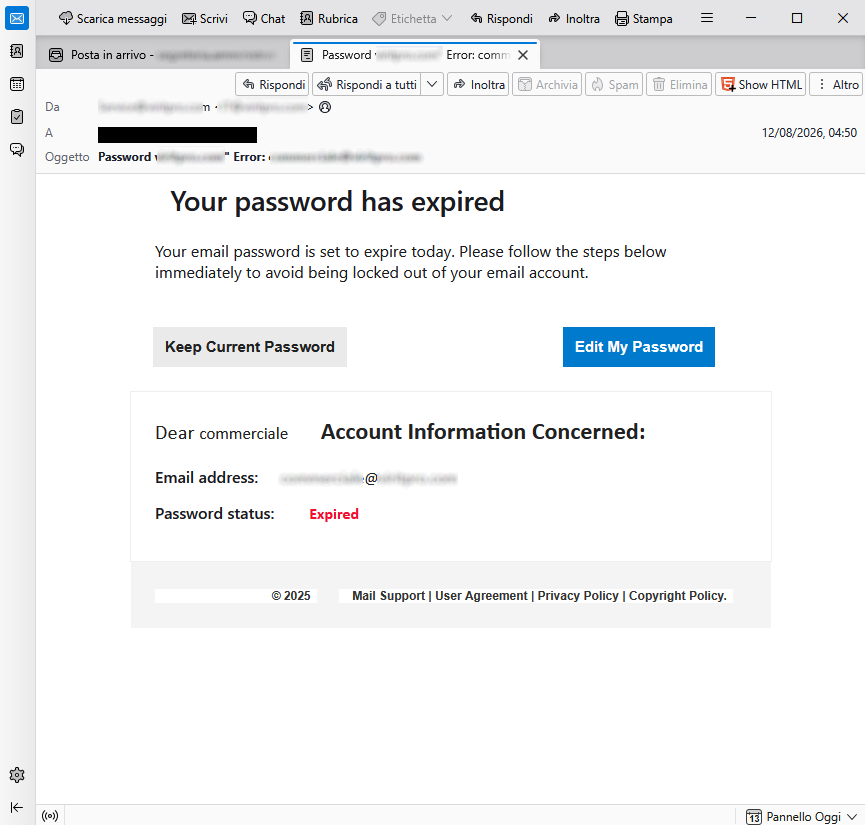
Below, we examine another phishing attempt aimed at stealing the victim’s email account credentials.
The message, in English, informs the recipient that their email password is due to expire today. It therefore urges them to follow the steps promptly via the link below to avoid losing access to their email account:
Edit My Password
When we examine the message, we see that it has a rather unusual email address that does not belong to the recipient’s email domain. This is decidedly unusual and should certainly arouse our suspicion.
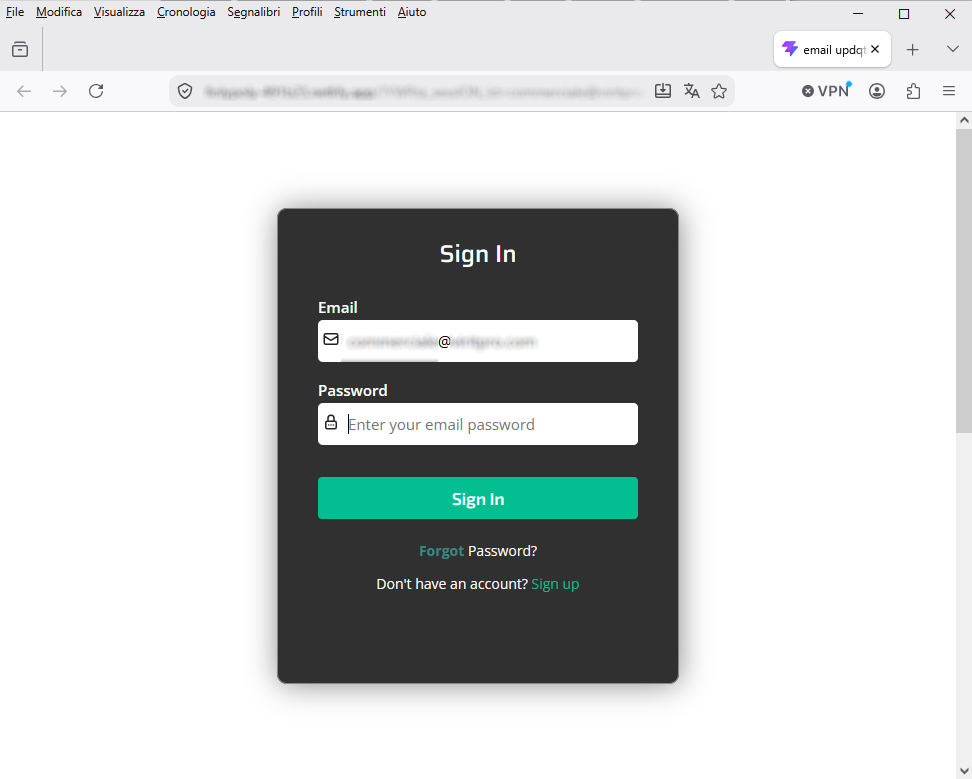
Anyone who inadvertently clicks on the link will be redirected to a suspicious website that mimics an email account login page.
On this page, users are asked to log in to their account by entering, specifically, their email password in order to download any pending messages and free up space.
Actually, the page where the user is redirected to enter their email account credentials is hosted on a suspicious address/domain, which is as follows:
https[:]//[FakeDomainName*]
We always urge you to pay attention to every detail, however trivial, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to a remote server and used by cybercriminals, with all the associated risks easily imaginable.
10 August 2026 ==> Phishing DHL
SUBJECT: <
DHL Delivery Notification: Shipment for xyz@xyz.com>
Below is a new phishing attempt, disguised as a fake message from the courier DHL, concerning the delivery of a supposed parcel.
The message, in English, informs the unsuspecting recipient that their parcel is due for delivery today: “
We are pleased to inform you that your parcel is due for delivery today. Please find the shipping documents attached for your reference. If you have any queries regarding the delivery or would like further information, please do not hesitate to contact us.”
These messages are increasingly being used to scam consumers who are making more and more purchases via e-commerce.
To proceed with the delivery, you must open the attachment named
DHL_Express_Tracking_921278975214451, which links to a web page.
The message has an email address unrelated to the
DHL domain; this is highly unusual and should certainly raise our suspicions. Anyone who clicks on the attachment will be redirected to a suspicious web page.
Although the landing page is visually misleading, it is hosted at a URL unrelated to the official
DHL domain.
On this page, users are prompted to log in to their account by entering their password.
The URL displayed in the browser address bar is unusual and cannot be traced back to the official domain.
https[:]//[FakeDomainName*]/....
If you enter your information on a fake website, it will be sent directly to the cybercriminals who created the scam and used for illegal purposes. We therefore recommend taking your time and carefully checking every detail—even seemingly trivial ones—when dealing with suspected online fraud.
09 August 2026 ==> Phishing GLS
SUBJECT: <
Notification of undelivered parcel ID: 320255908>
Below, we examine a new attempt at data theft that arrives via a deceptive message posing as the well-known courier company
GLS.
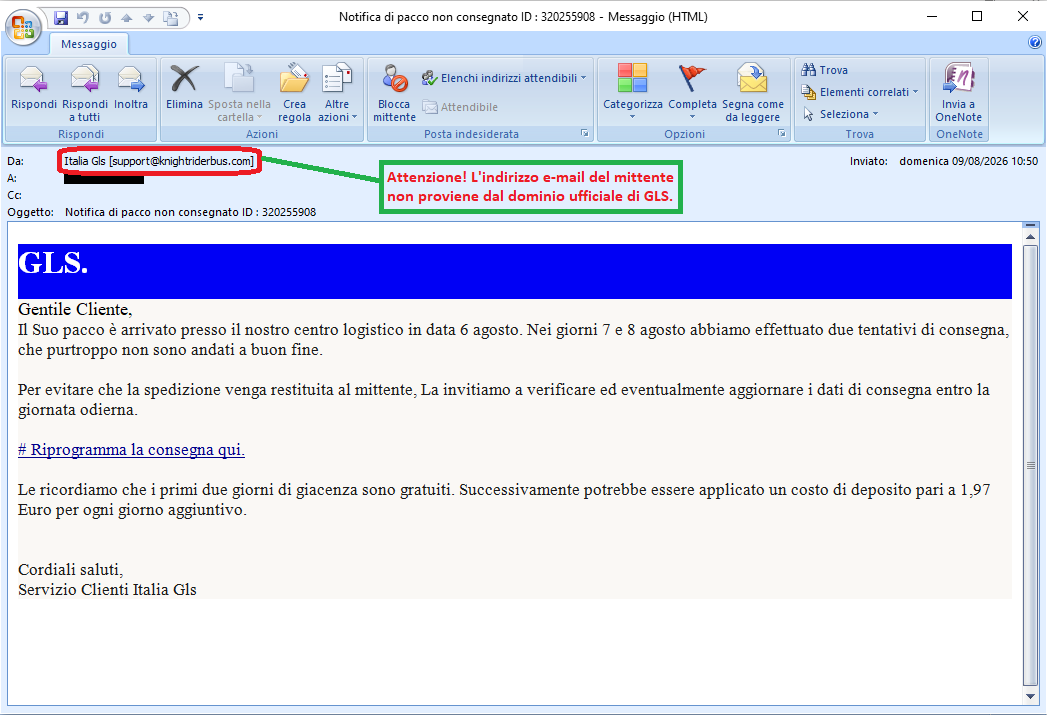
The message, shown on the side, refers to a parcel awaiting delivery. It states: “
Your parcel arrived at our logistics centre on 6 August. On 7 and 8 August, we made two attempts to deliver it, which unfortunately were unsuccessful.”
The recipient is therefore advised that, to prevent the parcel from being returned to the sender, they must check and, if necessary, update their delivery details by the end of today via the following link:
#Reschedule your delivery here
The message is very brief and lacks any information that would enable us to identify which parcel it refers to.
It also comes from an email address that is clearly not associated with the courier
GLS <
support(at)knightriderbus(dot)com>. This is highly unusual and should certainly arouse our suspicion.
GLS is clearly not involved in the mass distribution of these malicious campaigns, which are outright scams whose aim, as always, is to steal sensitive data from the unsuspecting recipient.
To avoid any unpleasant incidents, all it takes is a bit of care and a quick glance.
Anyone who unfortunately clicks on the link #Reschedule your delivery here here will be redirected to a web page that mimics the official GLS website, but which has already been reported as a SCAM SITE. It is, in fact, run by cybercriminals whose aim is to gain access to your most valuable personal data so that they can use it for illegal purposes.
We always encourage you to pay close attention to even the smallest details and never enter your personal information and/or passwords into forms hosted on fake websites, as they may be sent to a remote server and used by cybercriminals.
06 August 2026 ==> Phishing NETFLIX
SUBJECT: <
Netflix: Your account suspended please check now!>
This month, we examine the following phishing attempt, which originates from a fake message purporting to be from
NETFLIX – the well-known streaming platform for films, TV series and other paid content – and which aims to steal the victim’s credit card details.
The message informs the user that their account subscription has expired. It then asks them to update their account details as soon as possible so that they can continue to enjoy all the benefits on offer. The renewal process should be completed within 72 hours by clicking on the following link:
Review Your Account
On closer inspection of the message, we can see that it contains an email address that does not belong to the official
NETFLIX domain. This is highly unusual and should certainly raise our suspicions.
Anyone who, unfortunately, clicks on the
Review Your Account link
will be redirected to a suspicious web page.
From the image shown on the side, we can see that the web page where users are asked to log in to the platform is designed to look like the official NETFLIX website.
However, at a glance, we can see that the login page is hosted on an unusual address/domain.
https[:]//[FakeDomainName*]
If we continue with the registration process, we will probably be asked to enter our personal details and payment method, which will be used by cybercriminals, with all the associated risks that one can easily imagine.
05 August 2026 ==> Phishing Bank
SUBJECT: <
Urgent Notice: Account Suspension>
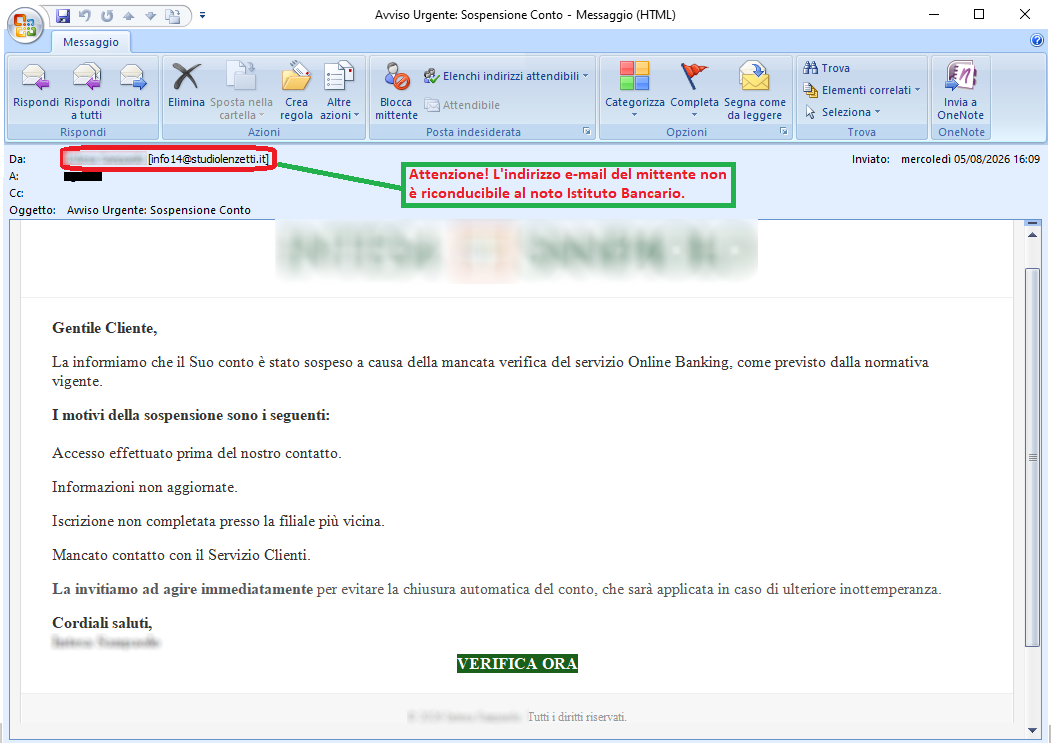
The message, using graphics stolen from or similar to those of a well-known bank, attempts to pass itself off as an official communication in order to induce the recipient to comply with the request and fall into this trap based on social engineering technique.
The message informs the recipient: “
Your account has been suspended due to failure to verify your Online Banking service, as required by current legislation.”
Activation of the new service is mandatory to prevent the account from being automatically closed. The reasons for the account suspension are also listed:
Logged in before we made contact.
Out-of-date information.
Registration not completed at the nearest branch.
Failure to contact Customer Services.
The user is therefore asked to follow the procedure via the following link:
CHECK NOW
We immediately notice that the alert message comes from a highly suspicious email address, <
info14(at)studiolenzetti(dot)it>, and contains very generic wording, despite featuring the bank’s logo to deceive the user. The aim is to trick the victim into logging in to their banking app so that their credentials can be stolen.
Anyone who, unfortunately, clicks on the
CHECK NOW link will be redirected to a suspicious web page, which has already been flagged as a deceptive page/website, as it is run by cybercriminals whose aim is to gain access to your most valuable data so that they can use it for their own purposes.
To conclude, we would urge you to always be wary of any email asking you to enter confidential information, and to avoid clicking on suspicious links, which could lead to a fake website that is difficult to distinguish from the genuine one.
04 August 2026 ==> Phishing Aruba
SUBJECT: <
Outstanding Payment – Settle the Debt to Avoid Account Deactivation>
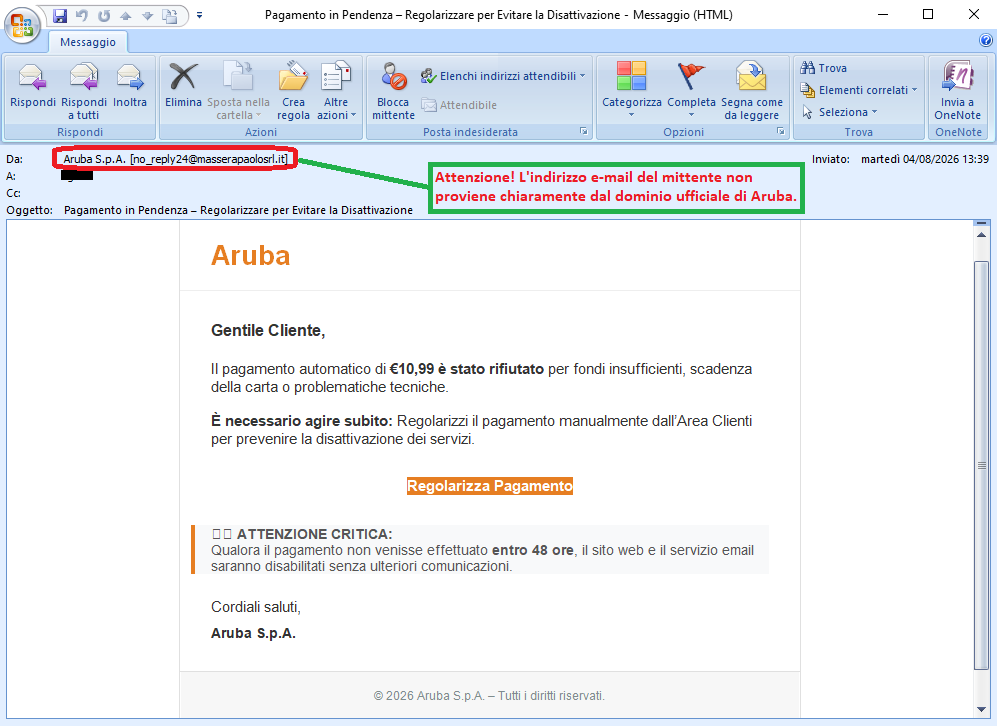
Below, we analyse another phishing attempt that purports to be a message from the
Aruba brand.
The message informs the recipient: “
The automatic payment of €10.99 has been declined due to insufficient funds, an expired card or technical issues.” It then asks them to make the payment within
48 hours in order to continue using the services hosted on
Aruba, via the following link:
Settle Payment
Always be cautious of requests to enter personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company
Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We can see straight away that the email address in the message does not belong to the official
Aruba domain <
no_reply24[at]masserapaolosrl[dot]it>. This is highly unusual and should certainly raise our suspicions.
Anyone who inadvertently selects the
Settle Payment link will be taken to a suspicious website that has already been identified as misleading. Cybercriminals manage the site to collect and exploit your personal data.
To conclude, we would urge you to always be wary of any email asking you to enter confidential information, and to avoid clicking on suspicious links, which could lead you to a fake website that is difficult to distinguish from the genuine one.
Therefore, always pay the utmost attention, and only ever log in via the official pages, not via suspicious links.
01 August 2026 ==> Phishing Webmail
SUBJECT: <
Email Notification: You have (6) pending messɑges>
Below, we examine another phishing attempt designed to steal the victim’s email account credentials.
The message, in English, informs the recipient that there are 6 messages waiting and that they can check their pending messages via the following link:
Release Pending Mails to inbox
On closer inspection of the message, we can see that it contains an email address that appears to come from the recipient’s own email account; this is a technique often used to conceal the real sender’s email address. This is highly unusual and should certainly raise our suspicions.
Anyone who unfortunately clicks on the link provided will be redirected to a fraudulent web page that mimics the email account login page.
On this page, the user is asked to log in to their account by entering, in particular, their email password in order to view any pending messages.
Actually, the page where the user is redirected to in order to enter their email account credentials is hosted on a suspicious address/domain, which is as follows:
https[:]//[FakeDomainName*]
We always urge you to pay attention to every detail, however trivial, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to a remote server and used by cybercriminals, with all the associated and easily imaginable risks.
A little attention and a quick glance can save you a lot of hassle and headaches
We urge you NOT to be fooled by these types of e-mails, which, even though they use familiar and not particularly sophisticated approach techniques, if there is a resurgence, with reasonable likelihood more than a few unfortunates will be fooled.
We invite you to check the following information on phishing techniques for more details:
09/07/2026 09:36 - Phishing: the most common credential and/or data theft attempts in July 2026...
12/06/2026 09:12 - Phishing: the most common credential and/or data theft attempts in June 2026...
12/05/2026 16:29 - Phishing: the most common credential and/or data theft attempts in May 2026...
02/04/2026 11:01 - Phishing: the most common credential and/or data theft attempts in April 2026.
04/03/2026 10:44 - Phishing: the most common credential and/or data theft attempts in March 2026.
04/02/2026 10:33 - Phishing: the most common credential and/or data theft attempts in February 2026.
08/01/2026 09:53 - Phishing: the most common credential and/or data theft attempts in January 2026.
04/12/2025 15:56
- Phishing: the most common credential and/or data theft attempts in December 2025.
04/11/2025 14:45
- Phishing: the most common credential and/or data theft attempts in Novembre 2025.
01/10/2025 16:40 - Phishing: the most common credential and/or data theft attempts in October 2025.
04/09/2025 09:45 - Phishing: the most common credential and/or data theft attempts in September 2025.
05/08/2025 08:58- Phishing: the most common credential and/or data theft attempts in August 2025.
Try Vir.IT eXplorer Lite
 If you are not yet using Vir.IT eXplorer PRO, it is advisable to install Vir.IT eXplorer Lite -FREE Edition- to supplement the antivirus in use to increase the security of your computers, PCs and SERVERS.
Vir.IT eXplorer Lite has the following special features:
- freely usable in both private and corporate environments with Engine+Signature updates without time limitation;
- fully interoperable with other AntiVirus software and/or Internet Security products (both free and commercial) already installed on your computer. It doesn't need any uninstallation and it doesn't cause slowdowns, as some features have been appropriately reduced to ensure interoperability with the AntiVirus software already on your PC/Server. This, however, allows cross-checking through the scan;
- it identifies and, in many cases, even removes most of the viruses/malware actually circulating or, alternatively, allows them to be sent to the C.R.A.M. Anti-Malware Research Center for further analysis to update Vir.It eXplorer PRO;
- through Intrusion Detection technology, also made available in the Lite version of Vir.IT eXplorer, the software is able to report any new-generation viruses/malware that have set in automatically and send the reported files to TG Soft's C.R.A.M
- Download Vir.IT eXplorer Lite from the official distribution page of TG Soft's website.
Acknowledgements
TG Soft's Anti-Malware Research Center would like to thank all users, customers, reseller technicians, and all people who have transmitted/reported material attributable to Phishing activities to our Research Center, that allowed us to make this information as complete as possible.
How to submit suspicious emails for analysis as possible phishing but also virus/malware or Crypto-Malware
You can submit materials to TG Soft's Anti-Malware Research Center safely and free of charge in two ways:
- any suspect email can be sent directly by the recipient's e-mail, to the following mail lite@virit.com,choosing as sending mode "Forward as Attachment" and inserting in the subject section "Possible phishing page to verify" rather than "Possible Malware to verify";
- save the e-mail to be sent to TG Soft's C.R.A.M. for analysis as an external file to the e-mail program used. The resulting file must be sent by uploading it from the page Send Suspicious Files (http://www.tgsoft.it/italy/file_sospetti.asp). Obviously if you want a feedback on the analysis of the data submitted, you have to indicate an e-mail address and a brief description of the reason for the submission (for example: possiible / probable phishing; possible / probable malware or other).
For more details on how to safely forward suspicious e-mails, we invite you to consult the following public page:
How to send suspicious emails for analysis
We provide all this information to help you prevent credential theft, viruses/malware or, even worse, next-generation Ransomware / Crypto-Malware.
TG Soft Anti-Malware Research Centre (C.R.A.M.)