PHISHING INDEX
Below are the most common email phishing attempts detected by the TG Soft Anti-Malware Research Center in
September 2026:
14/09/2026 =>
Klarna
09/09/2026 =>
Aruba - Suspended identity
03/09/2026 =>
Email account
02/09/2026 =>
Aruba
These emails aim to deceive unsuspecting victims into providing sensitive information, such as bank account details, credit card codes, or personal login credentials, with all the easily imaginable consequences.
14 September 2026 ==> Phishing Klarna
SUBJECT: <
[ Klarna.it ] (1) Confirm your contact details>
This month, we’re analysing a new phishing attempt that pretends to be a message from
Klarna, the Swedish payment service
.
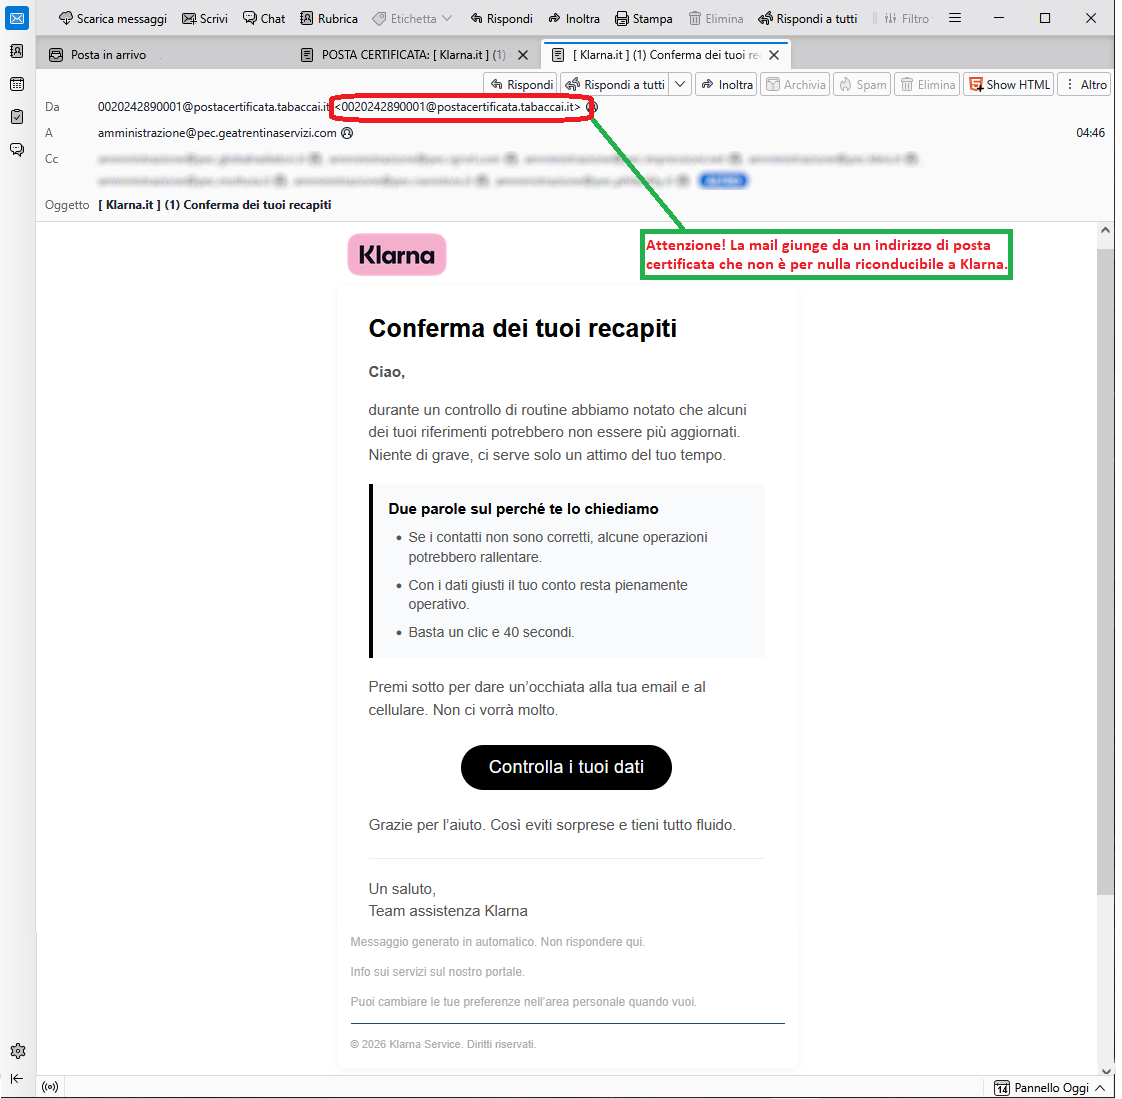
The message, which is sent via a certified email, informs the recipient that some of their personal details and/or contact information may not be up to date.
It therefore asks them to check their details and contact information – it only takes a few minutes – via the following link:
Check your data
The well-known online payment company,
Klarna, is clearly not involved in the mass sending of these emails, which are genuine scams whose aim, as always, is to steal sensitive data from the unsuspecting recipient.
On closer inspection of the message, there are a number of clues that should raise our suspicions. We immediately notice that the email address of the message, <
0020242890001[at]postacertificata[dot]tabaccai[dot]it>, does not belong to the official
Klarna domain – a fact that is decidedly unusual and should make us suspicious.
Anyone who, unfortunately, clicks on the
Check your data link will be redirected to a web page which, although it visually mimics the
Klarna account login page, has an unusual address/domain:
https[:]//[FakeDomainName*]
On this page, users are asked to log in to their customer area by entering their email address and password in order to retrieve their messages before they are deleted.
We always urge you to pay attention to every detail, however trivial, not to rush, and not to enter your personal details and/or passwords into forms hosted on fake web pages, as these will be sent to the cybercriminals behind the scam, who will use them for illegal purposes.
09 September 2026 ==> Phishing Aruba - Suspended identity
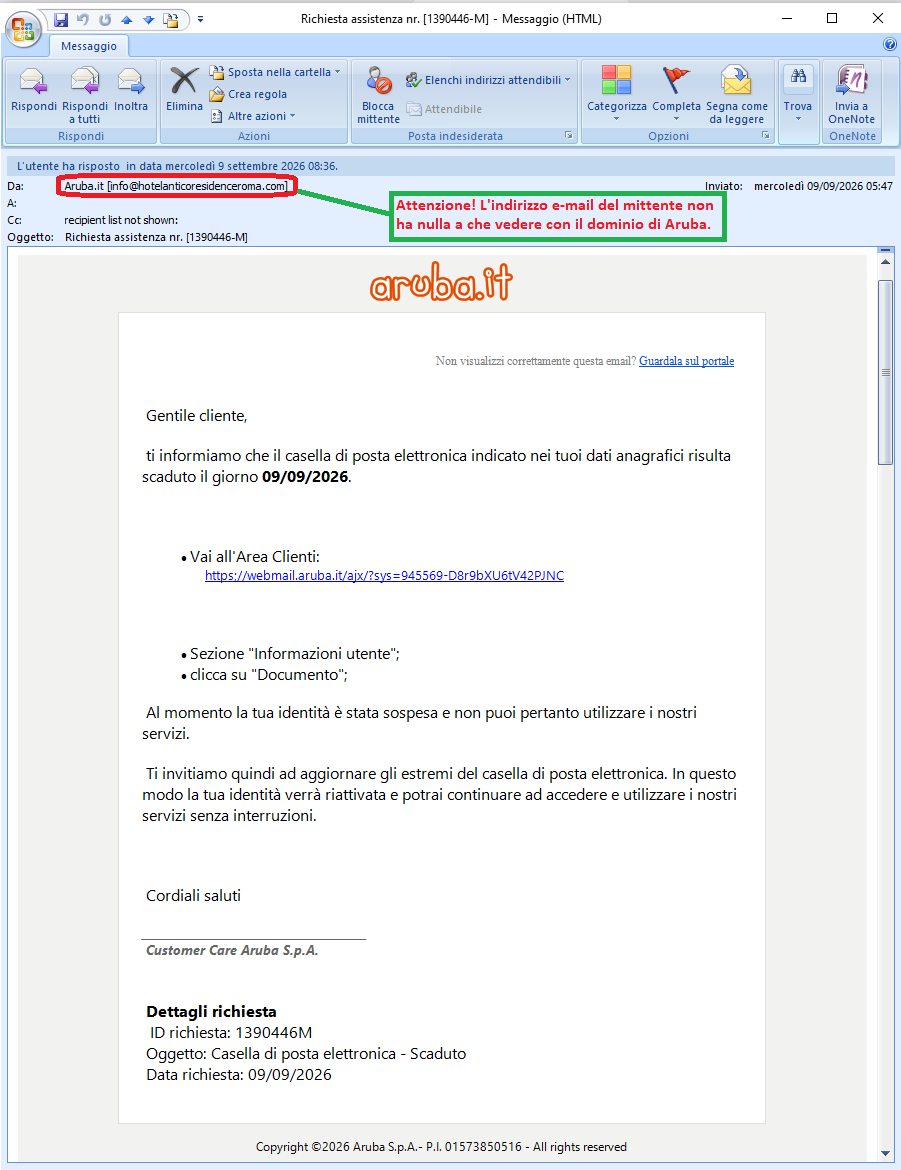
SUBJECT: <
Support request no. [1390446-M]>
Below, we analyse another phishing attempt that pretends to be a message from the
Aruba brand.
The message informs the recipient that their email account will expire on
09/09/2026. It states that their account has currently been suspended and that they are therefore unable to use the company’s services. It therefore asks them to update their account details in order to continue using the services hosted on Aruba, by logging into the customer portal via the following link:
https[:]//webmail[.]aruba[.]it/ajx/?sys=945569-D8r9bXU6tV42PJNC
We should always be wary of requests to enter personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We can see straight away that the email address in the message <
info[at]hotelanticoresidenceroma[dot]com> does not belong to the official
Aruba domain. This is highly unusual and should certainly raise our suspicions.
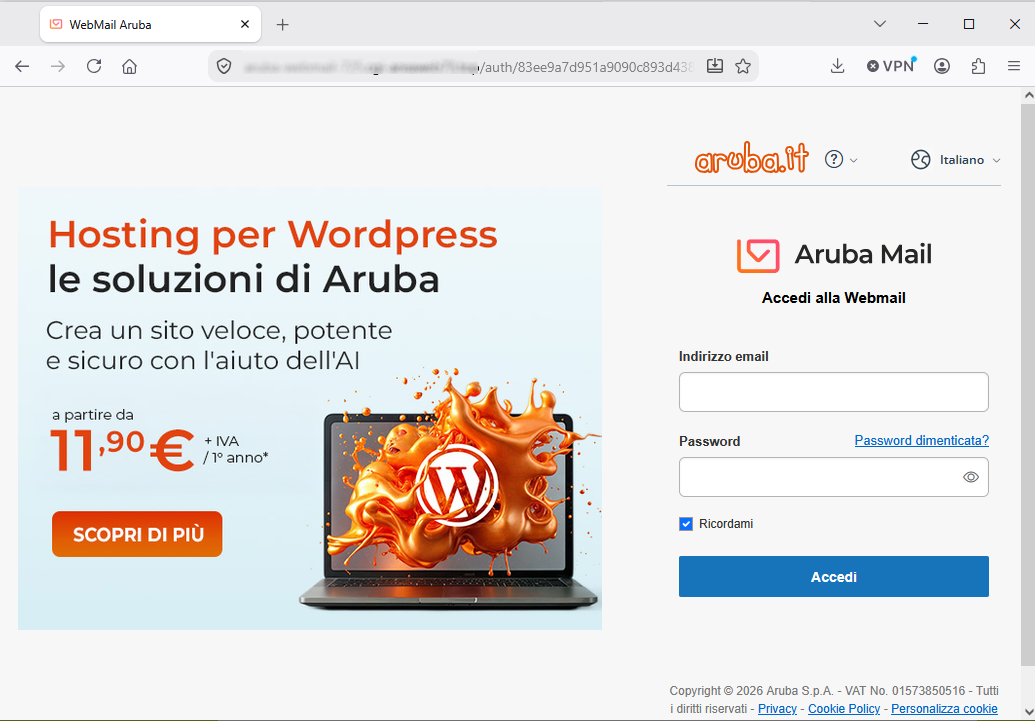
Anyone who unfortunately clicks on the link will be redirected to a web page which, although it visually mimics the
Aruba account login page – as evidenced by the presence of the well-known company’s logo – has an unusual address/domain:
https[:]//[FakeDomainName*]
On this page, users are asked to log in to their customer area by entering their email address and password. The aim of the cybercriminals behind this scam is clearly to gain hold of these details.
You should therefore always exercise the utmost caution, and only ever access the site via the official pages, not via suspicious links.
03 September 2026 ==> Phishing Email Account
SUBJECT: <
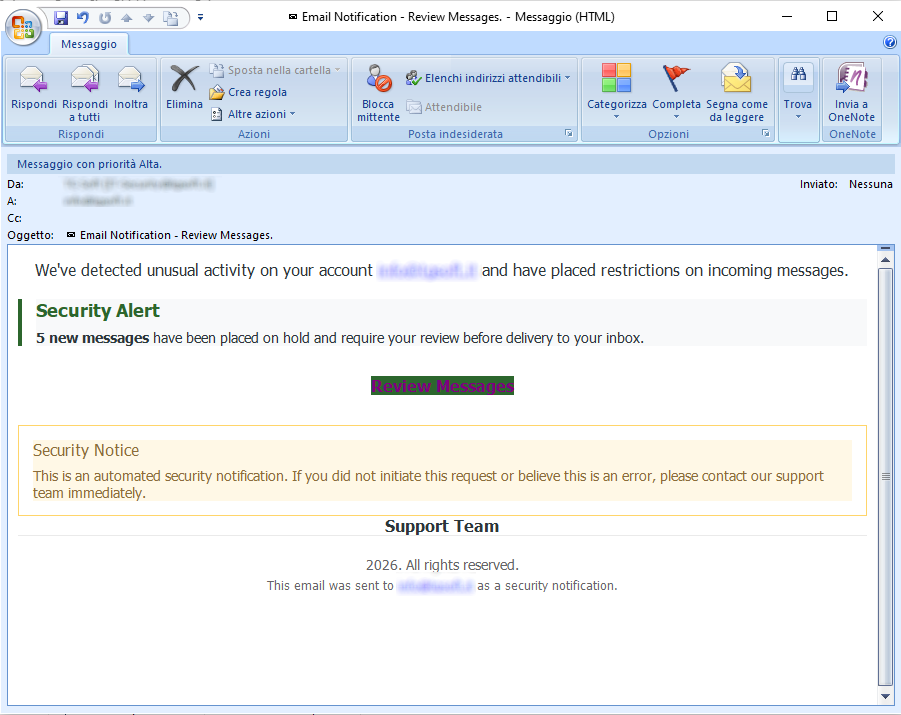
✉ Email Notification - Review Messages.>
Below, we analyse another phishing attempt aimed at stealing the victim’s email account credentials.
The message, in English, informs the recipient that unusual activity has been detected on their account and, for security reasons, their account has therefore been restricted. It then informs the user that, to restore normal service and retrieve any pending messages, they must click on the following link:
Review Messages
On closer inspection, we can see that the message has a rather unusual email address that appears to originate from the recipient’s email domain. This is decidedly unusual and should certainly raise our suspicions.
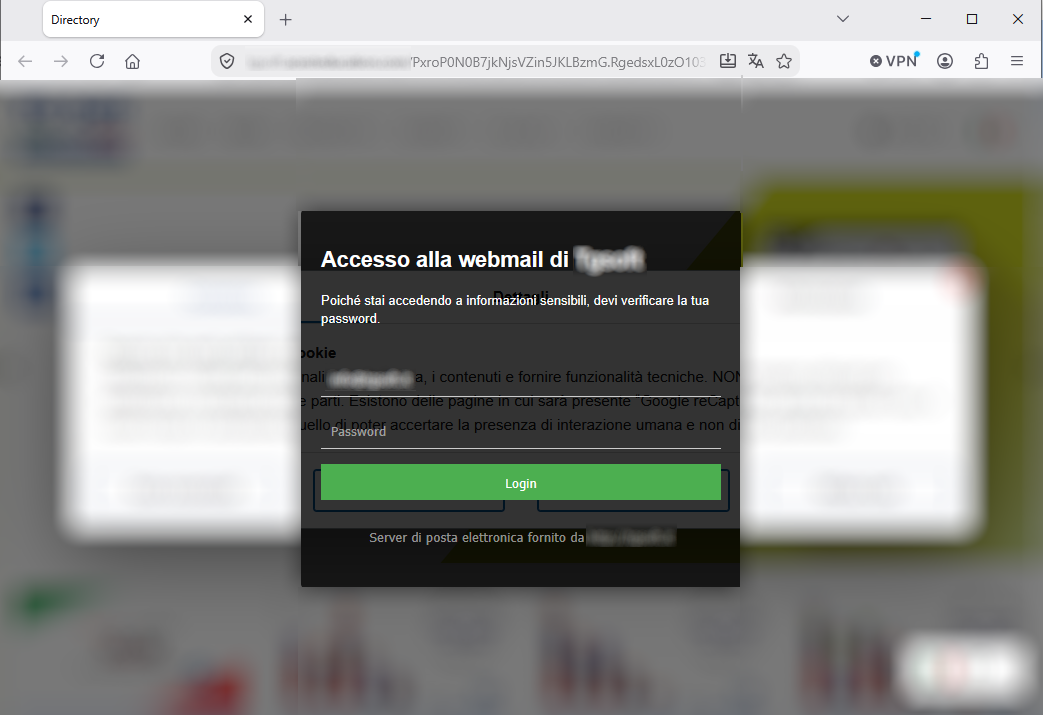
Anyone who unfortunately clicks on the link provided will be redirected to a fraudulent web page that mimics the email account login page.
On this page, users are asked to log in to their account by entering, in particular, their email password in order to retrieve any pending messages.
Actually, the page where you're redirected to enter your email account credentials is hosted on a suspicious address/domain, which is as follows:
https[:]//[FakeDomainName*]
We urge you always to pay attention to every detail, however trivial, and not to enter your personal details and/or passwords into forms hosted on fake websites, as these will be sent to a remote server and used by cyber-fraudsters, with all the associated and easily imaginable risks.
02 September 2026 ==> Phishing Aruba
SUBJECT: <
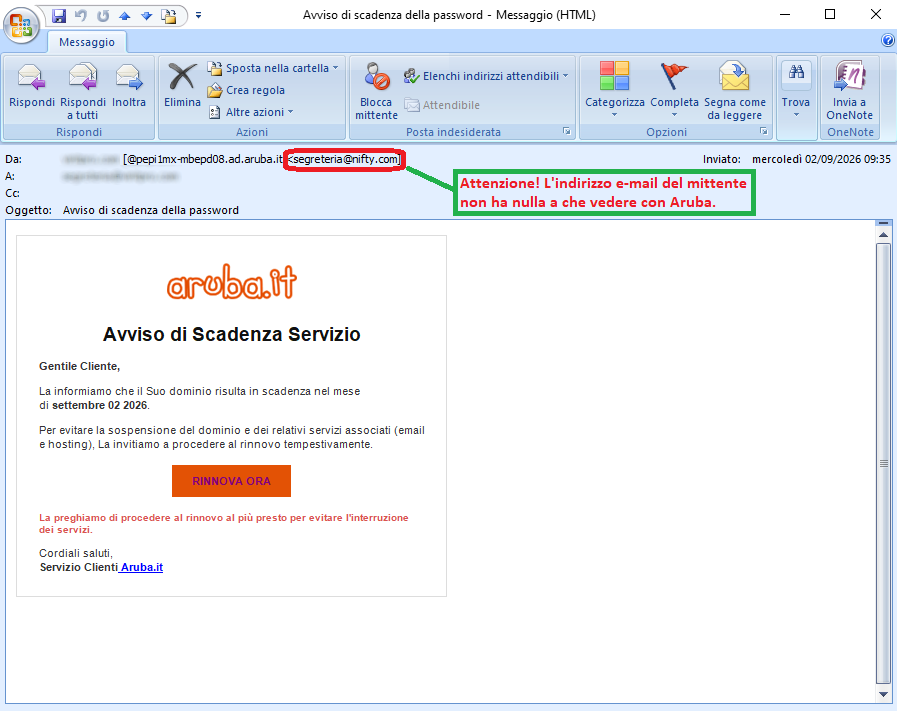
Password expiry notice>
Below, we analyse another phishing attempt that pretends to be a message from the
Aruba brand.
The message informs the recipient that their domain is due to expire in September 2026. It therefore urges them to renew it promptly, to avoid the suspension of the domain and the associated services, via the following link:
RENEW NOW
We should always be wary of requests to enter personal credentials via suspicious links sent by email.
The well-known web hosting, email and domain registration company
Aruba is clearly not involved in the mass sending of these emails, which are outright scams whose aim, as always, is to steal sensitive data from unsuspecting recipients.
We can see straight away that the email address in the message <
segreteria(at)nifty(dot)com> does not belong to the official Aruba domain. This is highly unusual and should certainly raise our suspicions.
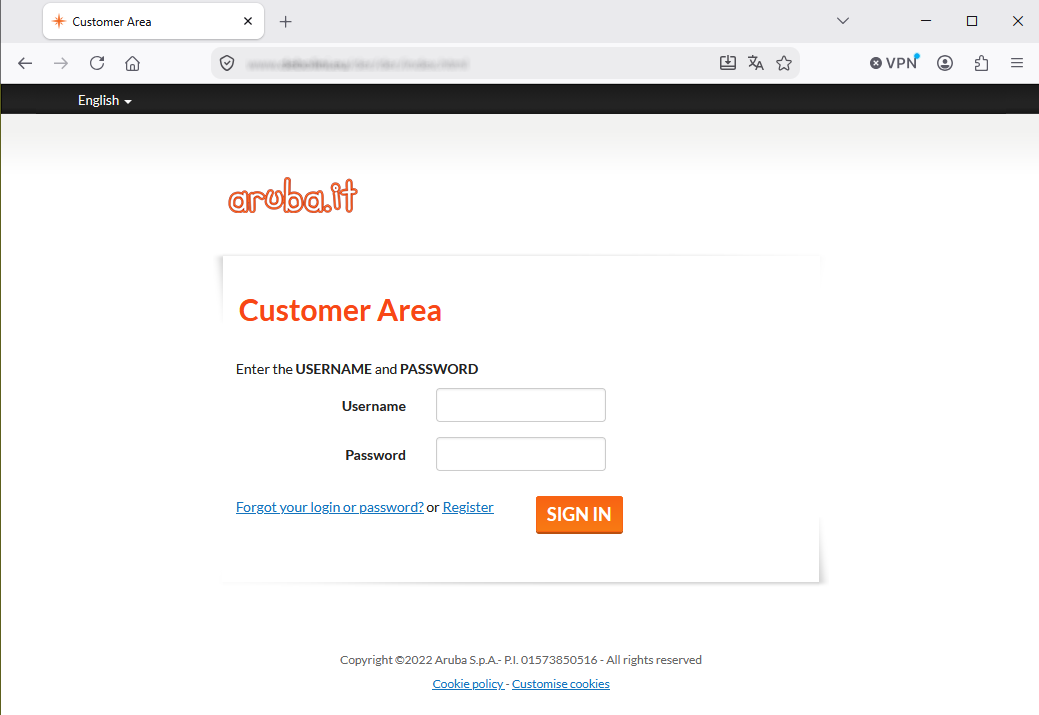
Anyone who unfortunately clicks on the
RENEW NOW link will be redirected to a web page which, although it visually mimics the
Aruba account login page – as evidenced by the presence of the well-known company’s logo – has an unusual address/domain:
https[:]//[FakeDomainName*]
On this page, users are asked to log in to their customer area by entering their email address and password. The aim of the cybercriminals behind this scam is clearly to gain hold of these details.
You should therefore always exercise the utmost caution, and only ever access the site via the official pages, not via suspicious links.
A little attention and a quick glance can save you a lot of hassle and headaches
We urge you NOT to be fooled by these types of e-mails, which, even though they use familiar and not particularly sophisticated approach techniques, if there is a resurgence, with reasonable likelihood more than a few unfortunates will be fooled.
We invite you to check the following information on phishing techniques for more details:
06/08/2026 12:04- Phishing: the most common credential and/or data theft attempts in August 2026...
09/07/2026 09:36 - Phishing: the most common credential and/or data theft attempts in July 2026...
12/06/2026 09:12 - Phishing: the most common credential and/or data theft attempts in June 2026...
12/05/2026 16:29 - Phishing: the most common credential and/or data theft attempts in May 2026...
02/04/2026 11:01 - Phishing: the most common credential and/or data theft attempts in April 2026.
04/03/2026 10:44 - Phishing: the most common credential and/or data theft attempts in March 2026.
04/02/2026 10:33 - Phishing: the most common credential and/or data theft attempts in February 2026.
08/01/2026 09:53 - Phishing: the most common credential and/or data theft attempts in January 2026.
04/12/2025 15:56
- Phishing: the most common credential and/or data theft attempts in December 2025.
04/11/2025 14:45
- Phishing: the most common credential and/or data theft attempts in Novembre 2025.
01/10/2025 16:40 - Phishing: the most common credential and/or data theft attempts in October 2025.
04/09/2025 09:45 - Phishing: the most common credential and/or data theft attempts in September 2025.
Try Vir.IT eXplorer Lite
 If you are not yet using Vir.IT eXplorer PRO, it is advisable to install Vir.IT eXplorer Lite -FREE Edition- to supplement the antivirus in use to increase the security of your computers, PCs and SERVERS.
Vir.IT eXplorer Lite has the following special features:
- freely usable in both private and corporate environments with Engine+Signature updates without time limitation;
- fully interoperable with other AntiVirus software and/or Internet Security products (both free and commercial) already installed on your computer. It doesn't need any uninstallation and it doesn't cause slowdowns, as some features have been appropriately reduced to ensure interoperability with the AntiVirus software already on your PC/Server. This, however, allows cross-checking through the scan;
- it identifies and, in many cases, even removes most of the viruses/malware actually circulating or, alternatively, allows them to be sent to the C.R.A.M. Anti-Malware Research Center for further analysis to update Vir.It eXplorer PRO;
- through Intrusion Detection technology, also made available in the Lite version of Vir.IT eXplorer, the software is able to report any new-generation viruses/malware that have set in automatically and send the reported files to TG Soft's C.R.A.M
- Download Vir.IT eXplorer Lite from the official distribution page of TG Soft's website.
Acknowledgements
TG Soft's Anti-Malware Research Center would like to thank all users, customers, reseller technicians, and all people who have transmitted/reported material attributable to Phishing activities to our Research Center, that allowed us to make this information as complete as possible.
How to submit suspicious emails for analysis as possible phishing but also virus/malware or Crypto-Malware
You can submit materials to TG Soft's Anti-Malware Research Center safely and free of charge in two ways:
- any suspect email can be sent directly by the recipient's e-mail, to the following mail lite@virit.com,choosing as sending mode "Forward as Attachment" and inserting in the subject section "Possible phishing page to verify" rather than "Possible Malware to verify";
- save the e-mail to be sent to TG Soft's C.R.A.M. for analysis as an external file to the e-mail program used. The resulting file must be sent by uploading it from the page Send Suspicious Files (http://www.tgsoft.it/italy/file_sospetti.asp). Obviously if you want a feedback on the analysis of the data submitted, you have to indicate an e-mail address and a brief description of the reason for the submission (for example: possiible / probable phishing; possible / probable malware or other).
For more details on how to safely forward suspicious e-mails, we invite you to consult the following public page:
How to send suspicious emails for analysis
We provide all this information to help you prevent credential theft, viruses/malware or, even worse, next-generation Ransomware / Crypto-Malware.
TG Soft Anti-Malware Research Centre (C.R.A.M.)